

MASTR · CRYPTO & WEB3
Smart accounts: recovery, delegation and the new control map
Programmable accounts can improve recovery and permissions, but the account’s validation rules become part of what the user must understand.
Kapiteltexte und technische Grafiken sind auf Englisch. Die Navigation ist in sieben Sprachen verfügbar.
Who can authorise spending, change the rules or recover the account?
An account can use more than one key rule
A smart account can define validation logic such as several signers, recovery conditions, spending limits or restricted permissions. These features can make everyday use more flexible, but they create a larger control surface than a single-key description suggests. The correct question is not whether smart accounts are categorically safer. It is whether the particular configuration matches the user’s needs and whether its controls are independently understandable.
ERC-4337 introduces a separate operation flow
ERC-4337 describes UserOperations handled through an EntryPoint contract and a bundler flow. Paymasters can participate in paying operation costs under defined rules. These roles should not be confused with possession of the user’s funds or with consensus validators. A sponsored operation is not costless in the economic sense; another party supplies or recovers the cost under the arrangement.
Delegation can change what a familiar address does
EIP-7702 specifies a mechanism for externally owned accounts to designate code. The security question therefore extends beyond whether the address looks like an ordinary key-controlled account. A delegation authorisation and the delegated implementation deserve review. The exact wallet behaviour depends on the deployed code and its controls, not simply the presence of the standard’s name in a product description.
Recovery is another authority path
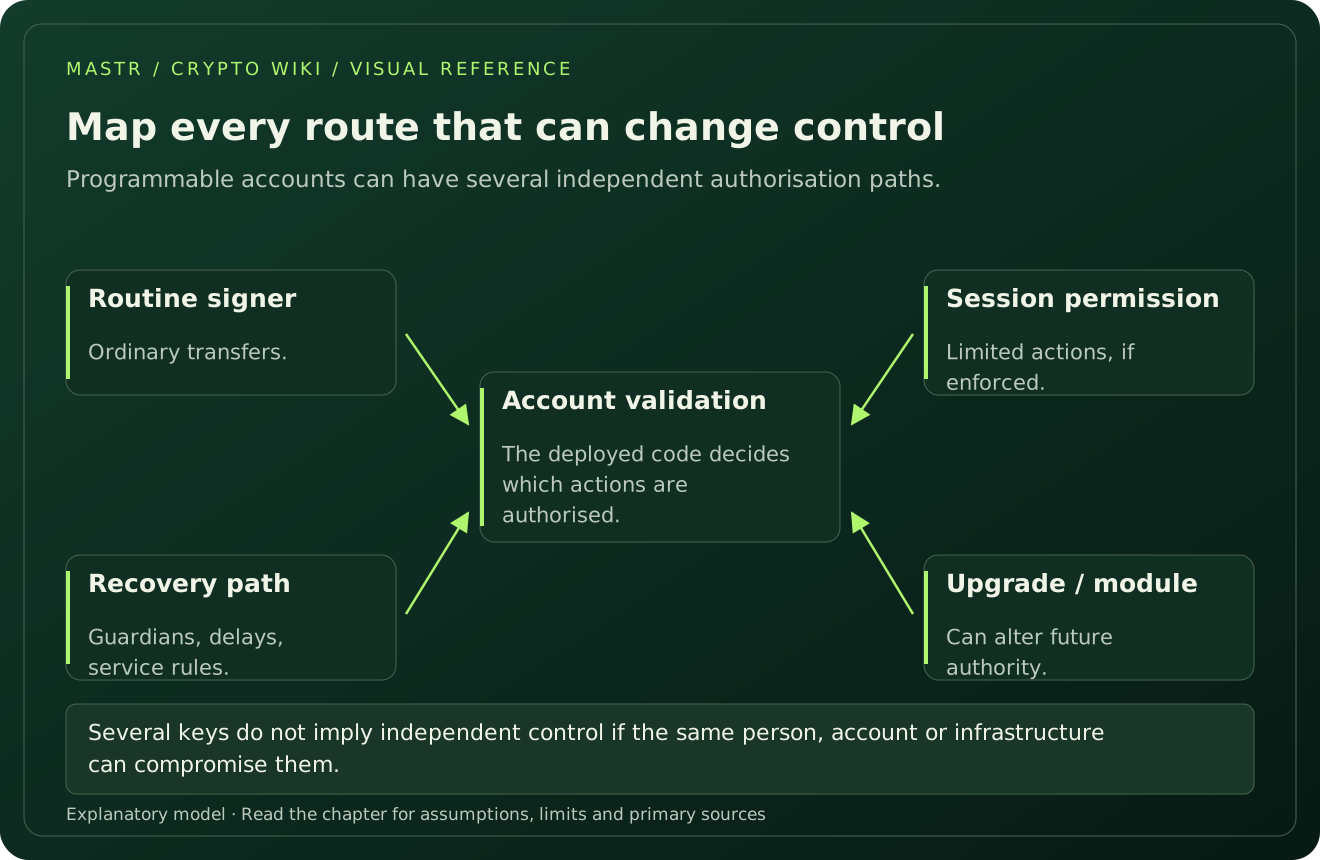
A recovery arrangement can involve guardians, a threshold, delays or a service. Document who can initiate and complete recovery, how a malicious recovery can be challenged and what happens when participants are unavailable. Several guardians using the same compromised cloud account may not be meaningfully independent. A recovery system that nobody has tested can fail when it is needed most.
Narrow permissions need enforceable boundaries
A session key can be limited by time, asset, action or amount if the implementation actually enforces those limits. A marketing statement that a key is restricted is not the restriction itself. Inspect modules, upgrade roles and emergency powers that can bypass ordinary validation. A complete control map includes the paths that change the rules, not only the path used for a routine transfer.
Erklärendes Beispiel
A game session is intended to authorise low-value game actions for one hour. If the delegated module can also install new modules or move unrelated assets, the effective permission is broader than the session label suggests. The implementation defines the boundary.
Fragen zum Mitnehmen
- Map every authorisation path.
- Read recovery and upgrade rules.
- Check that session limits are enforced.