Redes e infraestructura
Bitcoin’s security budget: the question behind the headline
MASTR’s discussion of mining incentives, the block subsidy and the long-term security-budget debate.
 MASTR
Primera publicación 4 min · 820 palabras
Original publication · 18 Apr 2025. Figures, claims and opinions reflect the original publication date.
Las publicaciones originales están en inglés. La navegación está disponible en siete idiomas.
Originally published as “IS Bitcoin’s Security Model Running Out of Time ⁉️”
An In-Depth Technical Analysis of Miner Incentives and Quantum Threats
1. Introduction: Bitcoin’s Original Security Model
#Bitcoin was launched in 2009 with a revolutionary idea: use Proof of Work (PoW) to secure a decentralized monetary system. PoW ensures that anyone wishing to tamper with the Bitcoin blockchain would need to expend immense computational energy, making attacks prohibitively expensive.
In Satoshi Nakamoto’s original whitepaper (2008), security was tied to the majority of CPU power being controlled by honest nodes, rather than any legal, institutional, or governance body. But this design relies on strong and economically rational miner incentives—a factor that's increasingly under threat.
2. Miner Economics: Why Bitcoin Is Secure—For Now
Bitcoin miners are rewarded in two ways:
- Block subsidy (newly minted BTC)
- Transaction fees
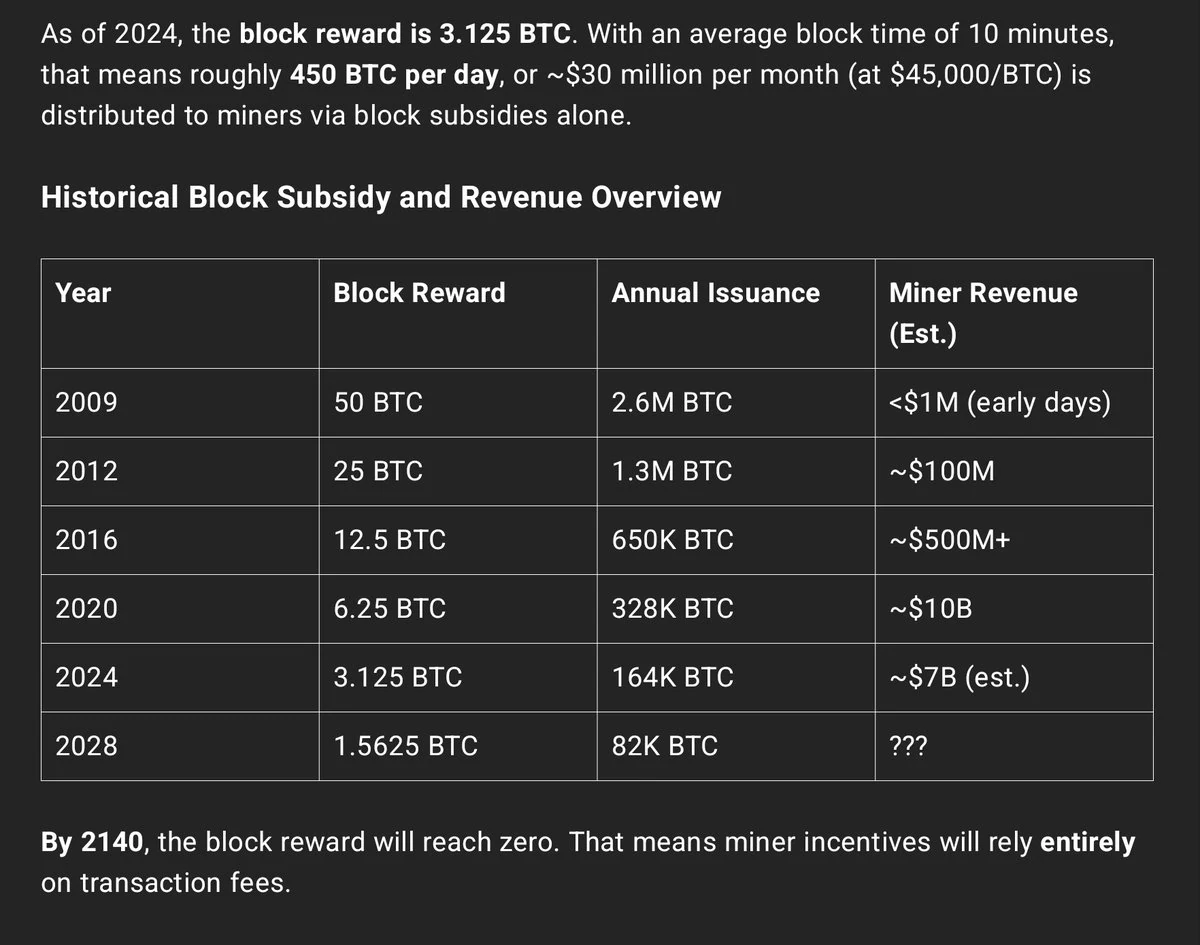
As of 2024, the block reward is 3.125 BTC. With an average block time of 10 minutes, that means roughly 450 $BTC per day, or ~$30 million per month (at $45,000/BTC) is distributed to miners via block subsidies alone.
Historical Block Subsidy and Revenue Overview
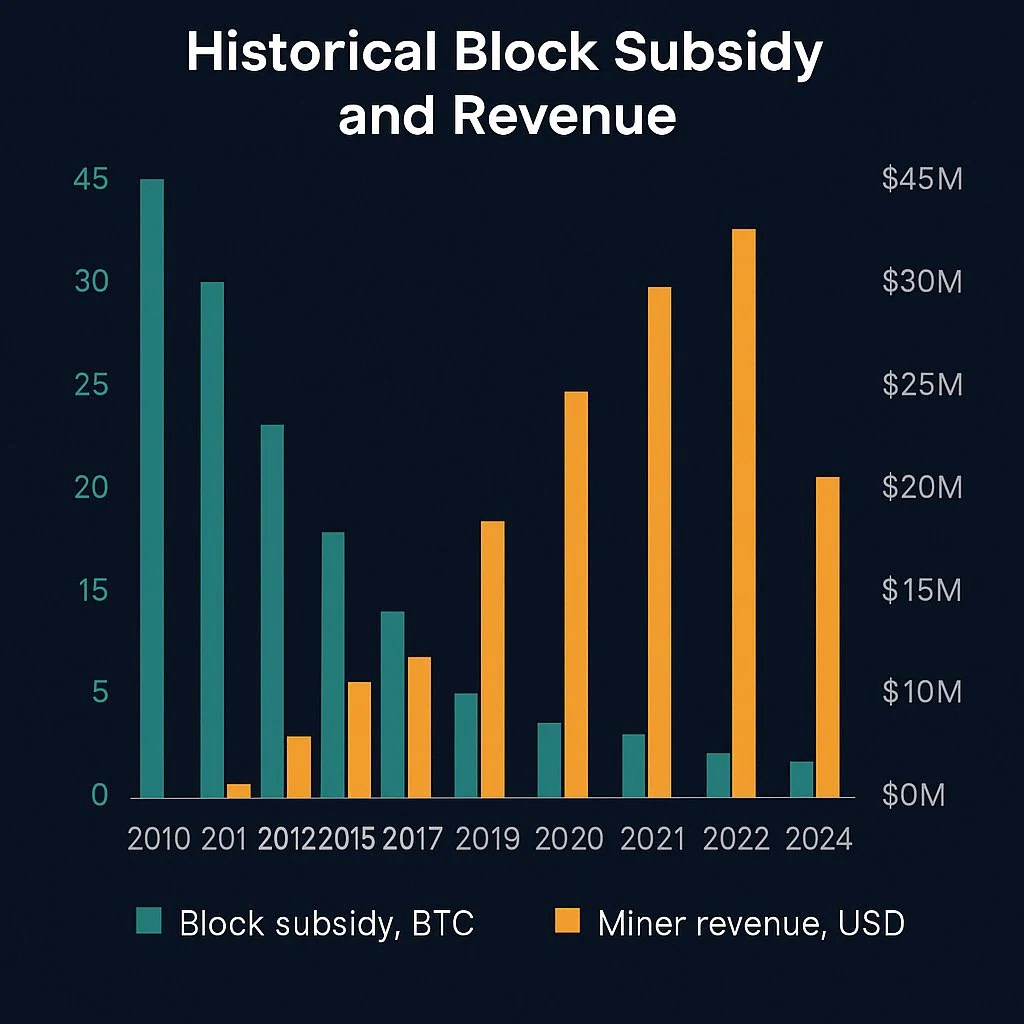
By 2140, the block reward will reach zero. That means miner incentives will rely entirely on transaction fees.
3. The Problem: Fee Markets Are Not Enough
Today, the average Bitcoin transaction fee is around $2–$3, though it spikes in bull markets. In 2021, during peak congestion, it briefly hit $60+, but that’s the exception, not the rule.
Current averages (2024):
- Block size: ~1.2 MB
- Transactions per block: ~2,500
- Fees per block: ~0.1–0.5 BTC
- Total daily fees: ~$150,000–$300,000
Compare that to $30 million per day in block subsidies, and you’ll see why this is a problem.
Without block rewards, Bitcoin would need to generate 100x higher fee volume just to maintain today’s security budget.
4. The Consequences of Declining Miner Revenue
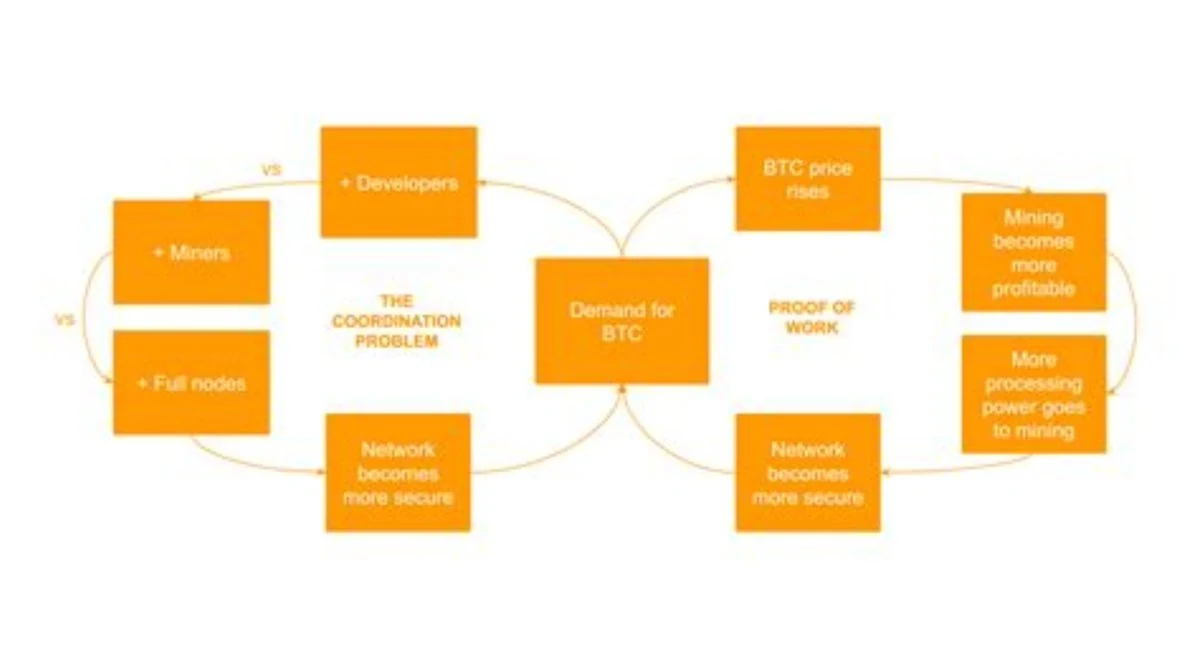
A. Security Budget Collapse
With lower income, fewer miners will be able to operate profitably. This leads to:
- Lower hash rate
- Easier 51% attacks
- More stale blocks (lower consensus quality)
- Greater vulnerability to mining cartels
B. Centralization Risk
Only the largest operations with access to:
- Cheap electricity
- Custom ASICs
- Political connections
...will survive. This shifts power away from decentralization, violating the core ethos of Bitcoin.
C. Selfish Mining & Strategic Withholding
If mining incentives drop, game-theoretic attacks become viable.
The 2014 paper by Eyal & Sirer introduced "Selfish Mining," showing that a miner with just 33% hash rate could manipulate the network to gain disproportionate rewards (Eyal & Sirer, 2014).
5. Enter Quantum Computing: The Cryptographic Threat
Bitcoin uses ECDSA (Elliptic Curve Digital Signature Algorithm) on the secp256k1 curve. This is secure against classical computers—but not quantum ones.
The threat: Shor’s Algorithm
Shor’s algorithm can factor large integers in polynomial time, breaking both RSA and ECC. That means:
- A quantum computer could extract your private key from your public key
- If your Bitcoin address has ever made a transaction, it’s exposed
Attack scenario:
- Attacker watches mempool
- Sees an outgoing transaction from your wallet
- Instantly calculates your private key
- Sends your funds to their address before your transaction confirms
This is called a “signature replay” attack.
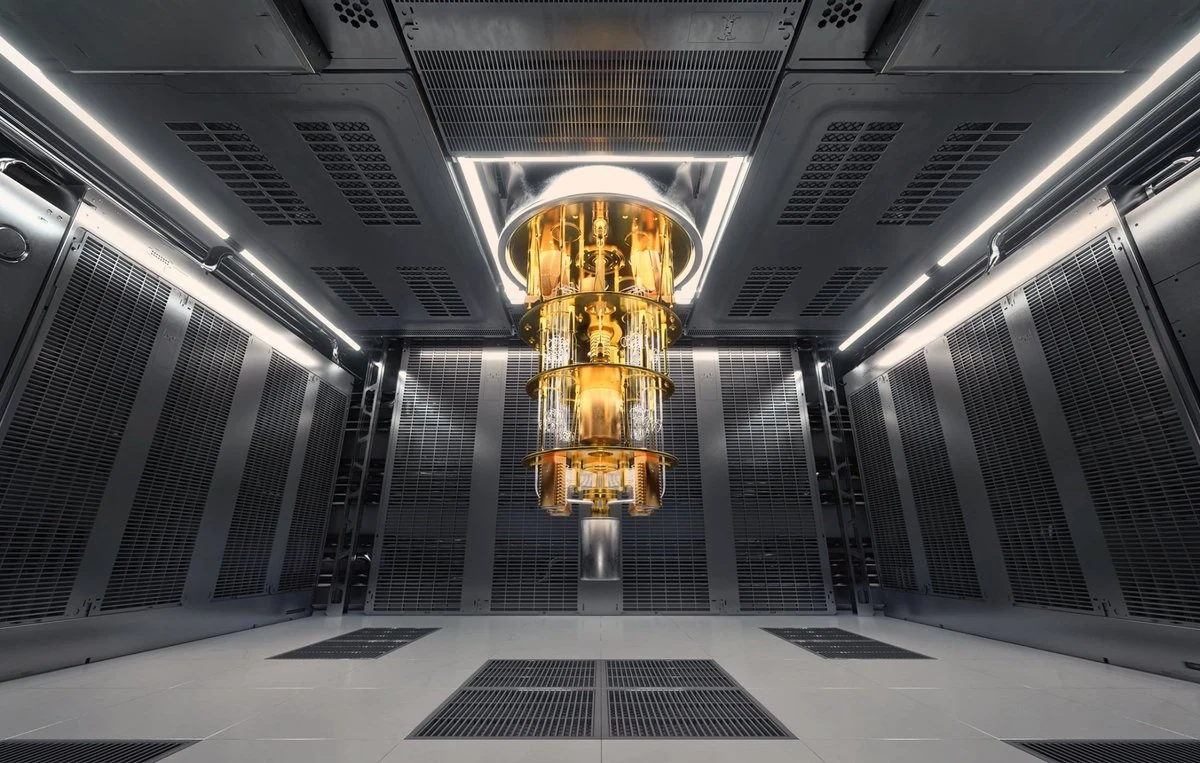
6. How Big Must a Quantum Computer Be?
To break Bitcoin's ECDSA-256:
- ~2,330 logical qubits
- ~10^12–10^13 quantum gates
- Error correction layers require ~1,000 physical qubits per logical qubit
→ Total: ~2–5 million physical qubits
The most advanced quantum chip as of 2024 (Google, IBM, IonQ) has:
- 100–433 physical qubits
- High decoherence
- Very high error rates
So… we’re safe?
For now, yes. But:
- IBM aims for 1,000+ qubits by 2025
- China’s spin-based systems are catching up
- Quantum-as-a-service platforms are scaling fast
- NIST is moving to standardize post-quantum algorithms by 2027 (NIST PQC Project)
7. How Bitcoin Could Respond
A. Post-Quantum Signatures
- Lattice-based schemes (e.g., CRYSTALS-Dilithium, Falcon, SPHINCS+)
- Zero-knowledge proof systems like STARKs and SNARKs
B. Address Hygiene
- Never reuse an address
- Move all old coins to new pay-to-pubkey-hash (P2PKH) addresses
- Ideally use taproot-only or quantum-hardened wallets
C. Soft Fork?
Bitcoin could adopt quantum-safe signature schemes via a soft fork, though it would be controversial and difficult to coordinate.
8. The Real Threat: Complacency
Bitcoin doesn't break overnight. It degrades slowly:
- Miner incentives drop
- Hash rate stagnates
- Attacks become easier
- Quantum capabilities creep forward
- Then, one day, a motivated attacker strikes
As the late Hal Finney once warned:
"The computer can be used as a tool to liberate and protect people, or enslave them."
The tools to protect Bitcoin exist. But we must act before they’re needed.
9. Final Thoughts
Bitcoin is antifragile—but only if its community stays vigilant.
The security budget cliff is real. The quantum threat is real. Neither are urgent… until they are. If Bitcoin is to survive the next 20 years as digital gold, it must adapt—economically and cryptographically.
Because math doesn’t care about ideology.
And quantum particles don’t wait for consensus.
Follow $MASTR to stay ahead of the curve.
Explore our other articles on crypto security, risk mitigation, and the future of decentralized trust.
The more you know, the safer you invest.
https://linktr.ee/askmastr.xyz