Histoire et chronologies
Crypto security incidents recorded in August 2026
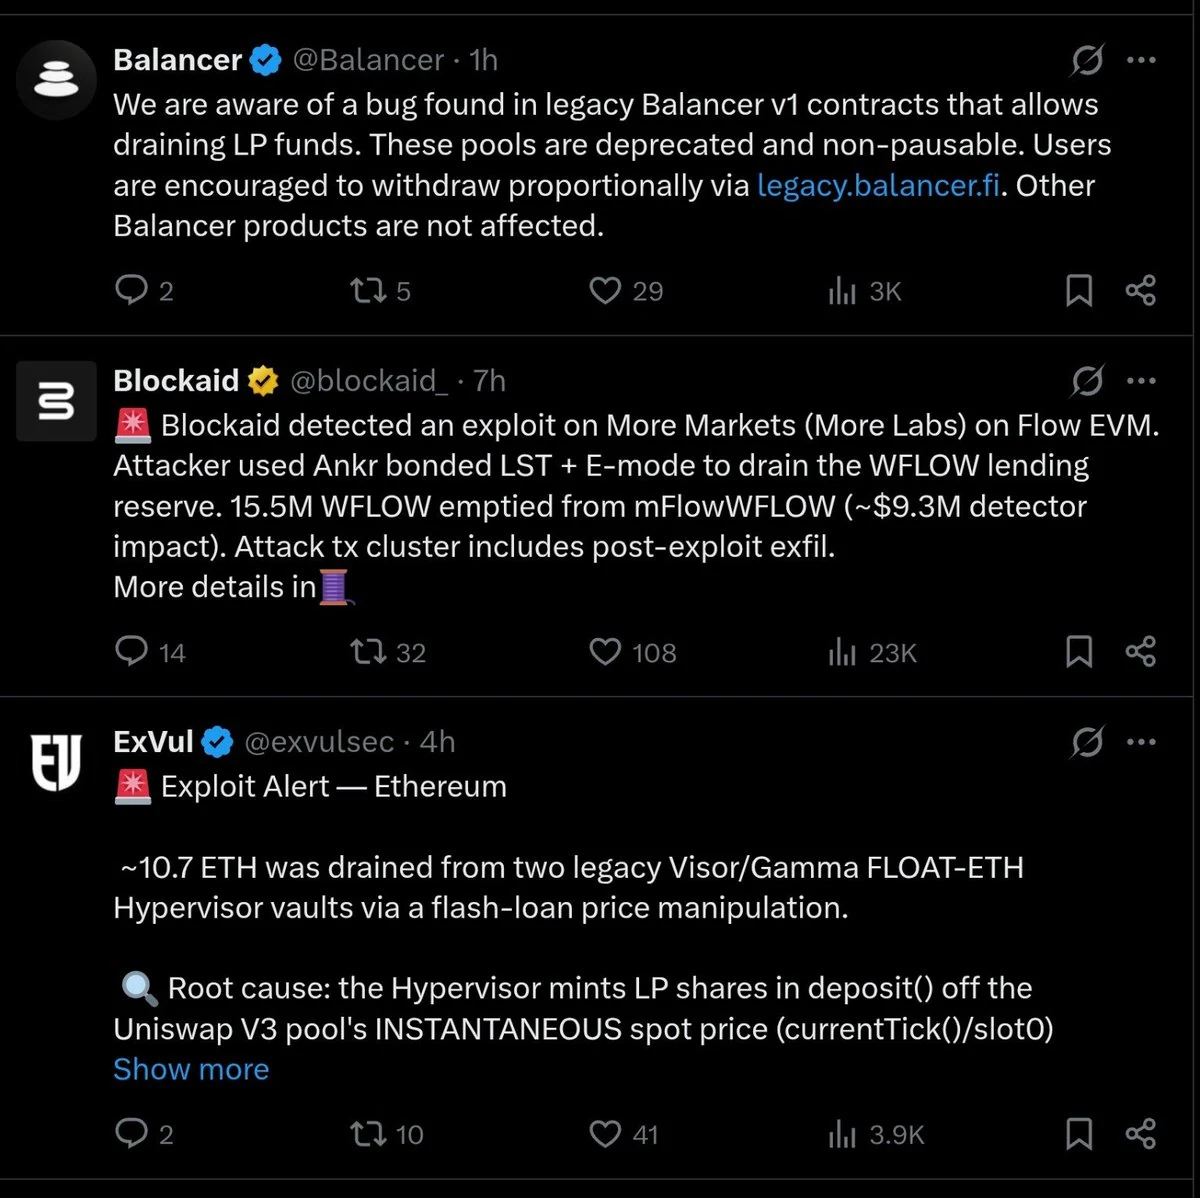
Aug 31, Balancer V1: Approximately $234K. A rounding flaw allowed 1 satoshi of WBTC input to mint 4,408.8 BPT after reserves were driven towards dust.
 MASTR
Première publication 6 min · 1,169 mots
Original publication · 31 Aug 2026. Figures, claims and opinions reflect the original publication date.
Les publications originales sont en anglais. La navigation est disponible en sept langues.
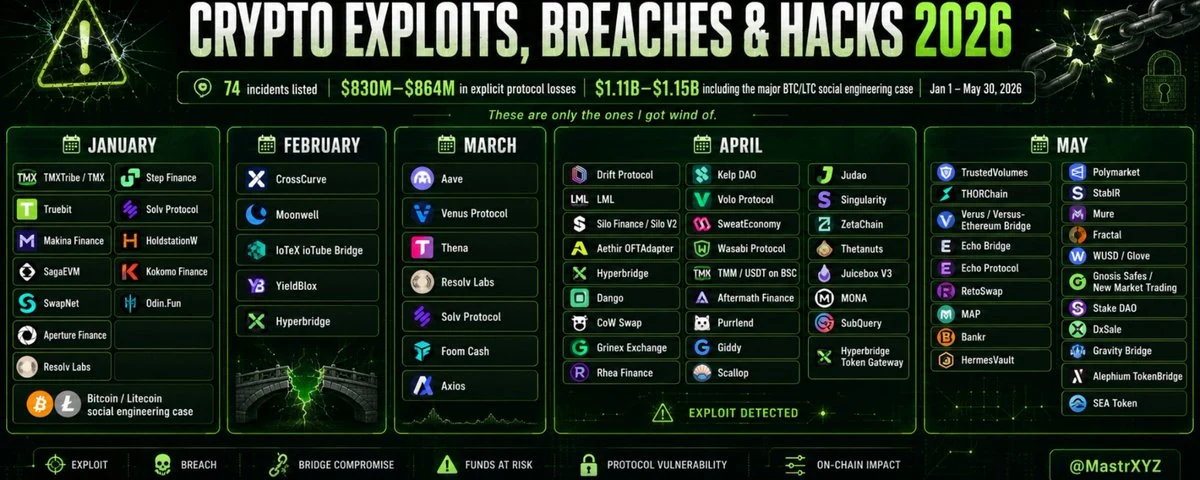
These are the crypto breaches, hacks and security incidents I could document from August 2026 alone.
This industry is run by degens.
Who could possibly be surprised?
....and I did not count the 1000 ordinary rug pulls or individual phishing scams per day.
August 2026:
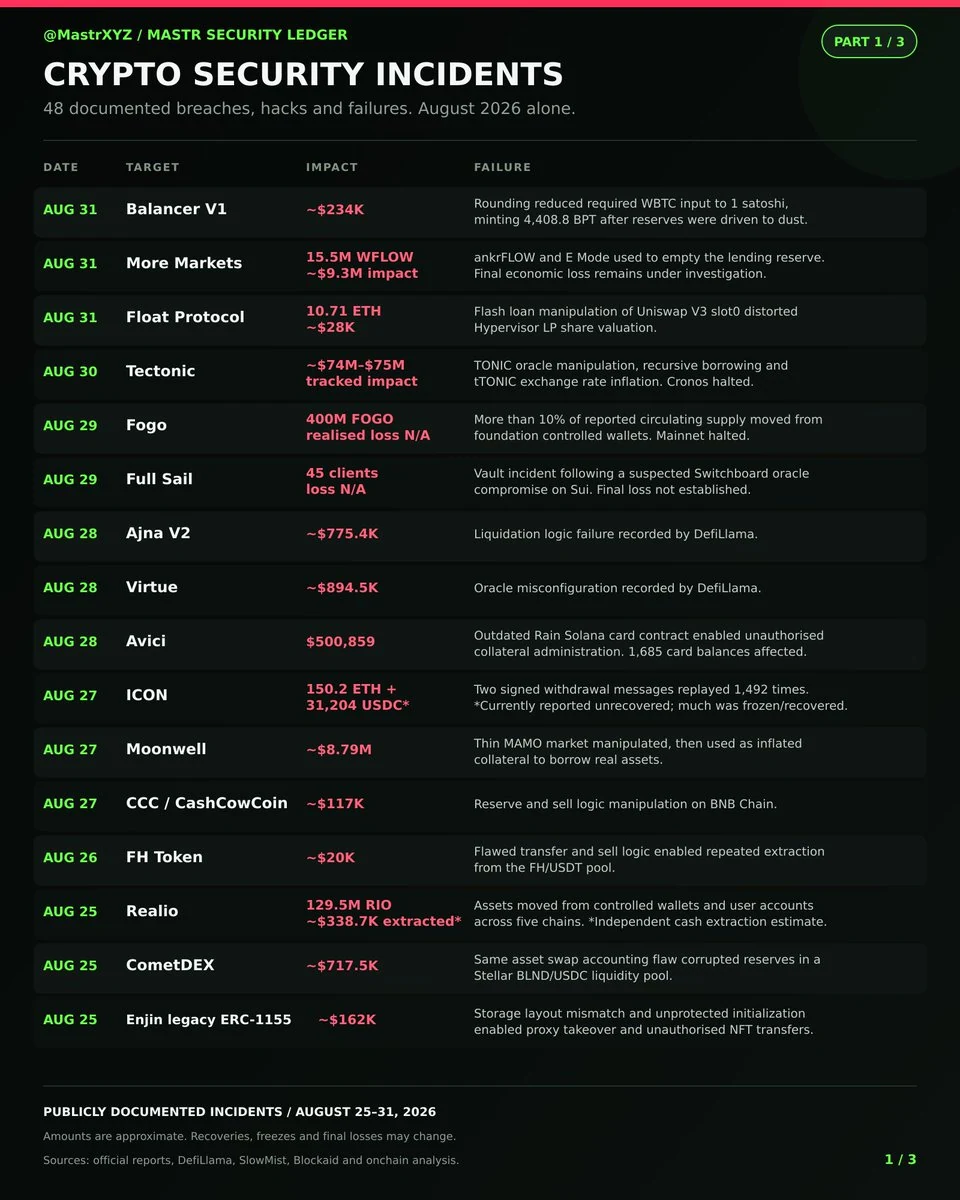
• Aug 31, Balancer V1: Approximately $234K. A rounding flaw allowed 1 satoshi of WBTC input to mint 4,408.8 BPT after reserves were driven towards dust.
• Aug 31, More Markets: 15.5M WFLOW removed from the lending reserve. Blockaid estimated approximately $9.3M impact. Final loss remains under investigation.
• Aug 31, Float Protocol: Approximately $28K or 10.71 ETH. Uniswap V3 slot0 manipulation distorted Hypervisor LP share valuations.
• Aug 30, Tectonic: Approximately $74M to $75M tracked impact after TONIC oracle manipulation, recursive borrowing and tTONIC exchange rate inflation. Cronos halted.
• Aug 29, Fogo: 400M FOGO, more than 10% of reported circulating supply, left foundation controlled wallets. Mainnet halted. Final realised loss remains unclear.
• Aug 29, Full Sail: Vault users affected after a suspected Switchboard oracle compromise on Sui. 45 clients reportedly affected. Final loss not established.
• Aug 28, Ajna V2: Approximately $775.4K recorded by DefiLlama from a liquidation logic failure.
• Aug 28, Virtue: Approximately $894.5K recorded by DefiLlama from an oracle misconfiguration.
• Aug 28, Avici: $500,859.22 removed from 1,685 card balances through an outdated Rain Solana card contract and unauthorised collateral administration. Self custodial wallets were unaffected.
• Aug 27, ICON: 2 legitimate signed withdrawal messages reportedly replayed 1,492 times, releasing 119.866M ICX and 531,600 bnUSD. Much was frozen or recovered. Approximately 150.2 ETH plus 31,204 USDC was reported as currently unrecovered.
• Aug 27, Moonwell: Approximately $8.79M in observed outflows after manipulation of the thin MAMO market.
• Aug 27, CCC / CashCowCoin: Approximately $117K through reserve and sell logic manipulation on BNB Chain.
• Aug 26, FH Token: Approximately $20K after flawed transfer and sell logic allowed repeated extraction from the FH/USDT pool.
• Aug 25, Realio: Roughly 129.5M RIO moved from controlled wallets and user accounts across 5 chains. Independent reconstruction estimated approximately $338.7K actually extracted by Aug 28.
• Aug 25, CometDEX: Approximately $717.5K after a same asset swap accounting flaw corrupted reserves in a Stellar liquidity pool.
• Aug 25, Enjin legacy ERC-1155: Approximately $162K through a storage layout mismatch and unprotected initialization path that enabled proxy takeover.
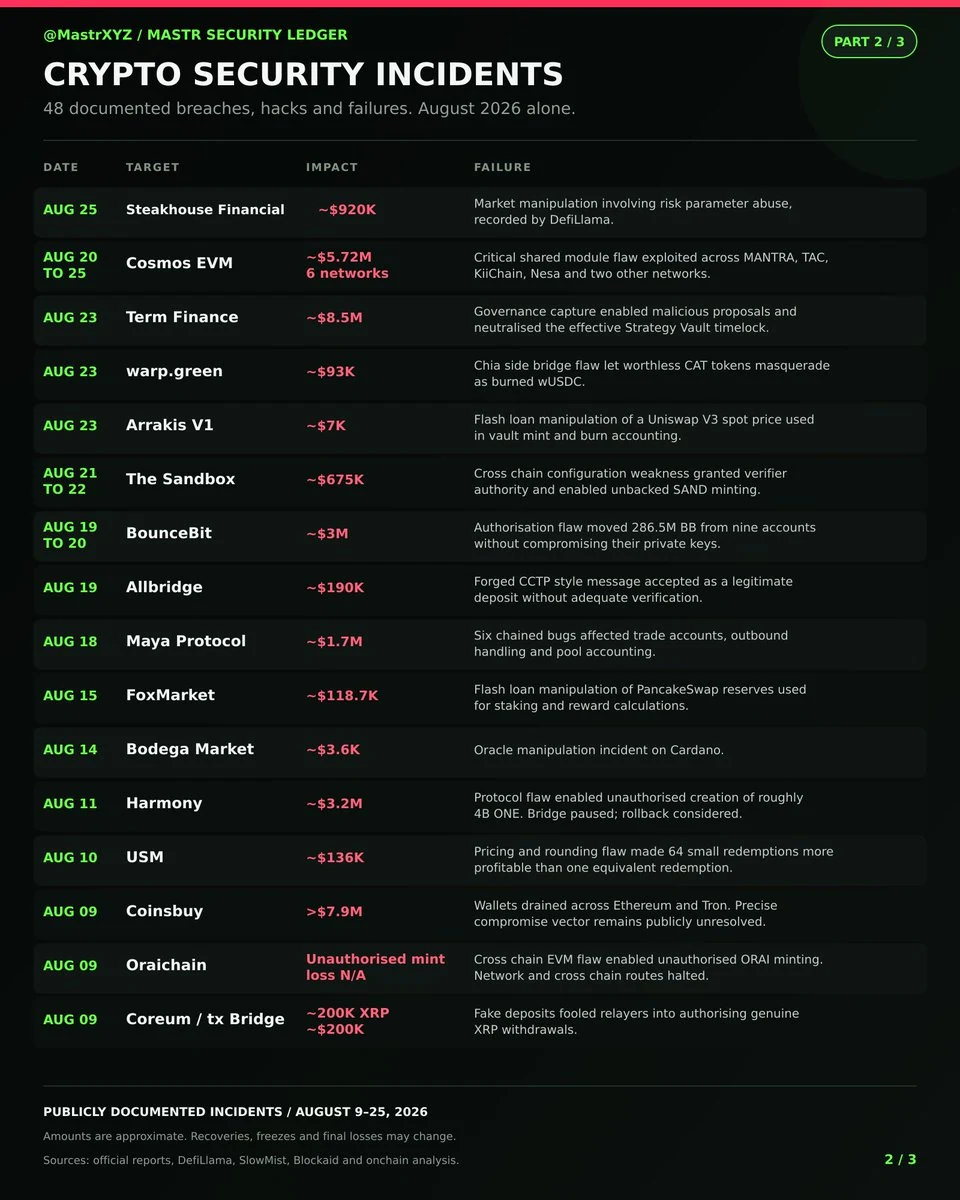
• Aug 25, Steakhouse Financial: Approximately $920K recorded by DefiLlama as market manipulation involving risk parameter abuse.
• Aug 20 to Aug 25, Cosmos EVM: The same critical vulnerability was exploited across 6 networks. Approximately $5.72M was converted through decentralised and centralised exchanges. MANTRA, TAC, KiiChain and Nesa were publicly linked to the exploit class.
• Aug 23, Term Finance: Approximately $8.5M drained after governance capture enabled malicious proposals and neutralised the effective timelock protecting Strategy Vaults.
• Aug 23, warp green: Approximately $93K after worthless CAT tokens were presented as burned wUSDC through a Chia side bridge logic flaw.
• Aug 23, Arrakis V1: Approximately $7K through flash loan manipulation of a Uniswap V3 spot price used in vault mint and burn accounting.
• Aug 21 to Aug 22, The Sandbox: Approximately $675K after a cross chain configuration weakness gave the attacker verifier authority and enabled unbacked SAND minting.
• Aug 19 to Aug 20, BounceBit: Approximately $3M after an authorisation flaw allowed 286.5M BB to be moved from 9 accounts without compromising their private keys. The affected standalone L1 was subsequently retired.
• Aug 19, Allbridge: Approximately $190K after a forged CCTP style message was accepted as a legitimate deposit.
• Aug 18, Maya Protocol: Approximately $1.7M through 6 chained bugs affecting trade accounts, outbound handling and pool accounting.
• Aug 15, FoxMarket: Approximately $118.7K through flash loan manipulation of PancakeSwap reserves used for staking and reward calculations.
• Aug 14, Bodega Market: Approximately $3.6K, classified by DefiLlama as an oracle manipulation incident on Cardano.
• Aug 11, Harmony: Approximately $3.2M recorded loss after a protocol flaw enabled unauthorised creation of roughly 4B ONE. The bridge was paused and rollback options were considered.
• Aug 10, USM: Approximately $136K after a pricing and rounding flaw made 64 smaller redemption calls more profitable than 1 equivalent redemption.
• Aug 9, Coinsbuy: More than $7.9M drained from wallets across Ethereum and Tron. The precise compromise vector remains publicly unresolved.
• Aug 9, Oraichain: A cross chain EVM vulnerability enabled unauthorised ORAI minting. The network and cross chain routes were halted. No reliable final dollar loss has been published.
• Aug 9, Coreum / tx Bridge: Almost 200,000 XRP, approximately $200K, drained after fake deposits fooled relayers into authorising genuine XRP withdrawals.
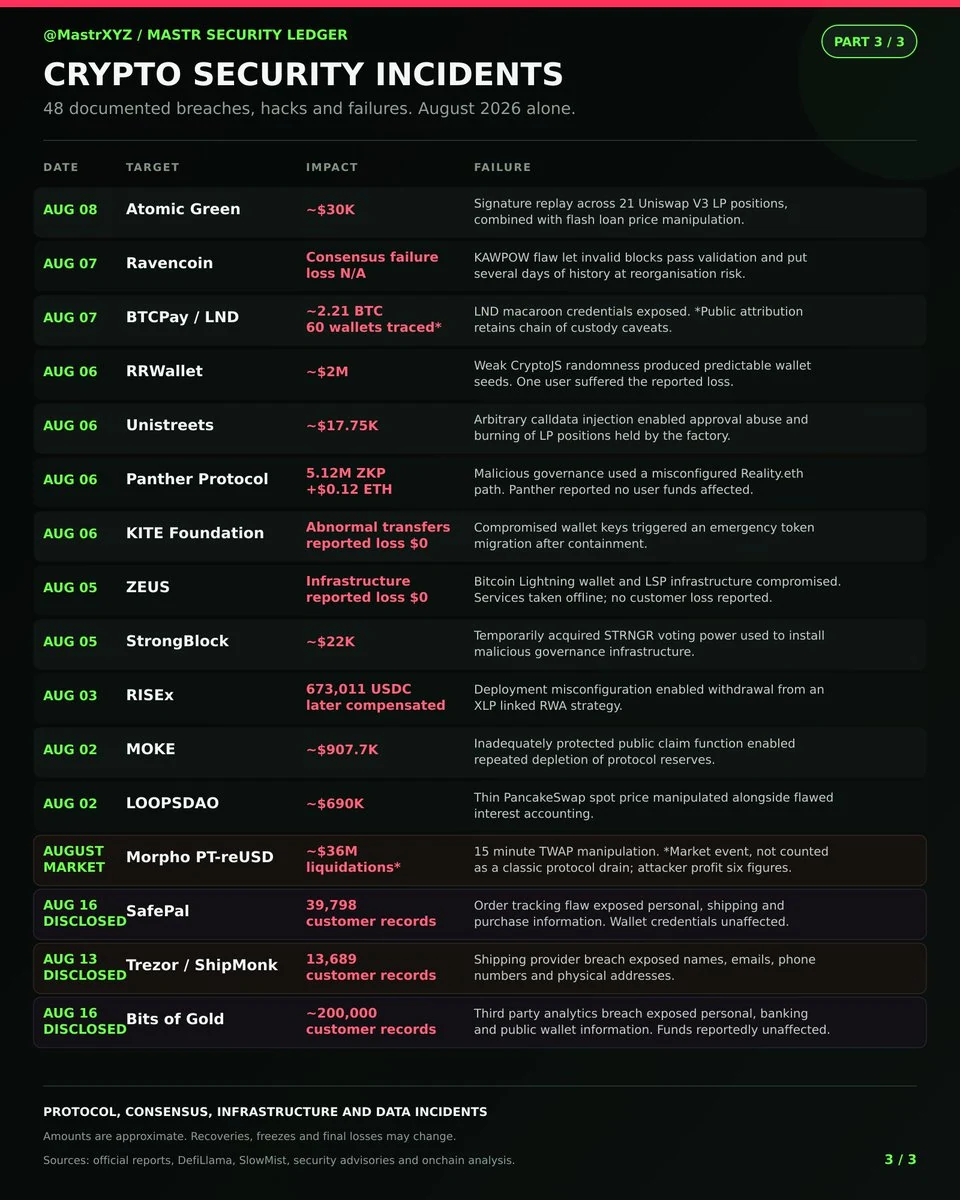
• Aug 8, Atomic Green: Approximately $30K through signature replay across 21 Uniswap V3 LP positions combined with flash loan price manipulation.
• Aug 7, Ravencoin: A critical KAWPOW consensus flaw allowed invalid blocks to pass validation and placed several days of transaction history at risk of reorganisation. No simple theft figure captures the impact.
• Aug 7, BTCPay Server / LND: A vulnerability exposed LND macaroon credentials. Independent analysis traced approximately 2.21 BTC from 60 wallets to 2 collector addresses, with attribution caveats remaining.
• Aug 6, RRWallet: Approximately $2M lost by 1 user after weak CryptoJS randomness produced predictable wallet seeds.
• Aug 6, Unistreets: Approximately $17,750 through arbitrary calldata injection that allowed approvals to be abused and LP positions burned.
• Aug 6, Panther Protocol: 5.12M ZKP and 0.12 ETH removed through malicious governance on a misconfigured Reality.eth execution path. DefiLlama records approximately $7,578 of loss. Panther said no user funds were affected.
• Aug 6, KITE Foundation: Compromised wallet keys triggered abnormal transfers and an emergency token migration. No user or project asset loss was reported after containment.
• Aug 5, ZEUS: Infrastructure compromise affecting the Bitcoin Lightning wallet and LSP provider. Services were taken offline. No customer fund loss was reported.
• Aug 5, StrongBlock: Approximately $22K through a governance takeover using temporarily acquired STRNGR voting power.
• Aug 3, RISEx: 673,011 USDC withdrawn from an XLP linked RWA strategy because of a deployment misconfiguration. Depositors were later compensated.
• Aug 2, MOKE: Approximately $907.7K after an inadequately protected public claim function allowed repeated depletion of protocol reserves.
• Aug 2, LOOPSDAO: Approximately $690K through manipulation of a thin PancakeSwap spot price combined with flawed interest accounting.
OTHER AUGUST SECURITY DAMAGE NOT COUNTED AS CLASSIC PROTOCOL DRAINS
• Morpho PT-reUSD: Manipulation involving a 15 minute TWAP caused approximately $36M in liquidations. This was not a conventional protocol drain, and attacker profit was reportedly in the 6 figure range.
• SafePal: Personal and shipping information belonging to 39,798 hardware wallet customers exposed through an order tracking flaw.
• Trezor / ShipMonk: Personal information belonging to 13,689 customers exposed through a shipping provider breach.
• Bits of Gold: Personal information reportedly belonging to approximately 200,000 customers exposed through compromised third party analytics infrastructure.
Several incidents remain under investigation, and totals may change because of recoveries, freezes, revised valuations and conflicting tracker methodologies.