Storia e cronologie
Crypto breaches and scandals: the first half of 2026
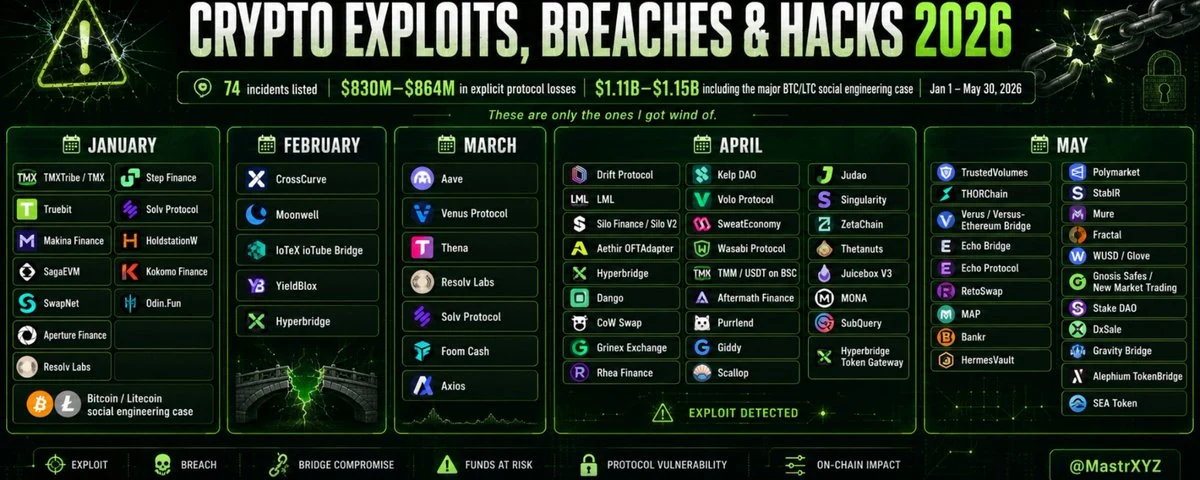
I listed only public bigger incidents, breaches, exploits, scams, fraud buckets and major crypto security scandals below.
 MASTR
Prima pubblicazione 14 min · 2,883 parole
Original publication · 1 Jul 2026. Figures, claims and opinions reflect the original publication date.
Le pubblicazioni originali sono in inglese. La navigazione è disponibile in sette lingue.
Half a Year of Madness.
My Counted and Known Crypto Breaches, Hacks, Exploits and Scandals From January 1, 2026 to July 1, 2026.
I listed only public bigger incidents, breaches, exploits, scams, fraud buckets and major crypto security scandals below.
Total damage across all numerically counted entries:
around $1.36B to $1.47B
Read through it and learn.
And before anyone says “you missed Pumpfun rugs and CEX scams": yes, obviously.
Based on the long-run average of more than 21,000 tokens per day, @Pumpfun likely added at least 3.5 million to 4 million new tokens from January 1, 2026 to mid June 2026 alone.
It is millions of dead tokens, with roughly 2.4 million to 2.8 million dying the same day and roughly 2.8 million to 3.2 million dying within 2 days.
Estimated Pumpfun dead-token / rug damage:
around $300M to $900M+++
This list is already obscene without counting every individual memecoin rug and CEX inside scam;
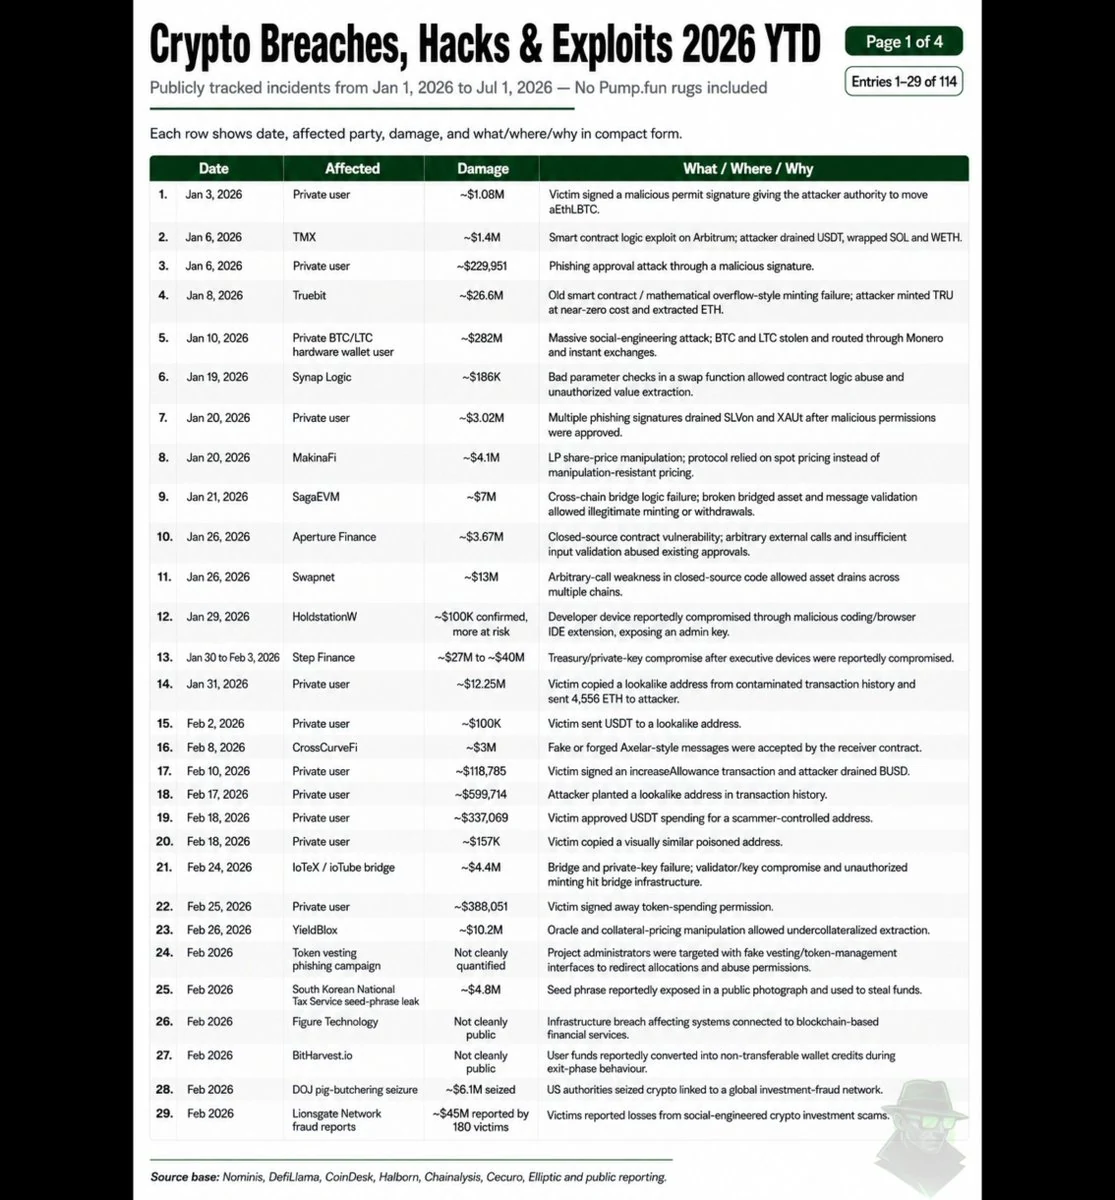
➡️ January 3, 2026: Private user
Damage: ~$1.08M
What happened: Phishing attack. The victim signed a malicious permit signature that gave the attacker authority to move aEthLBTC.
➡️ January 6, 2026: TMX
Damage: ~$1.4M
What happened: Smart contract logic exploit on Arbitrum. The attacker abused flawed contract logic and drained USDT, wrapped SOL and WETH.
➡️ January 6, 2026: Private user
Damage: ~$229,951
What happened: Phishing approval attack. Another malicious signature, another wallet drained.
➡️ January 8, 2026: Truebit
Damage: ~$26.6M
What happened: Old smart contract / mathematical overflow-style minting failure. The attacker minted TRU at almost no cost and extracted ETH.
➡️ January 10, 2026: Private BTC/LTC hardware wallet user
Damage: ~$282M
What happened: Massive social engineering attack. BTC and LTC were stolen and moved through Monero and instant exchanges. Hardware wallet, huge funds, still destroyed by human-process failure.
➡️ January 19, 2026: Synap Logic
Damage: ~$186K
What happened: Smart contract vulnerability. Bad parameter checks in a swap function allowed contract logic abuse and unauthorized value extraction.
➡️ January 20, 2026: Private user
Damage: ~$3.02M
What happened: Multiple phishing signatures. The attacker drained SLVon and XAUt after the victim approved malicious permissions.
➡️ January 20, 2026: MakinaFi
Damage: ~$4.1M
What happened: LP share-price manipulation. The protocol relied on spot pricing instead of manipulation-resistant pricing.
➡️ January 21, 2026: SagaEVM
Damage: ~$7M
What happened: Cross-chain bridge logic failure. Broken bridged asset and message validation allowed illegitimate minting or withdrawals.
➡️ January 26, 2026: Aperture Finance
Damage: ~$3.67M
What happened: Closed-source contract vulnerability. Arbitrary external calls and insufficient input validation allowed attackers to abuse existing approvals.
➡️ January 26, 2026: Swapnet
Damage: ~$13M
What happened: Same ugly vulnerability family as Aperture. Arbitrary-call weakness in closed-source code let attackers drain assets across multiple chains.
➡️ January 29, 2026: HoldstationW
Damage: ~$100K confirmed, more at risk
What happened: Private key compromise. A developer device was reportedly compromised through a malicious coding/browser IDE extension, exposing an admin key.
➡️ January 30 to February 3, 2026: Step Finance
Damage: ~$27M to ~$40M, commonly cited around $30M
What happened: Treasury/private-key compromise. Executive devices were reportedly compromised, allowing attackers to access wallets controlled by the project.
➡️ January 31, 2026: Private user
Damage: ~$12.25M
What happened: Address poisoning. The victim copied a lookalike address from contaminated transaction history and sent 4,556 ETH to the attacker.
➡️ February 2, 2026: Private user
Damage: ~$100K
What happened: Address poisoning. The victim sent USDT to a lookalike address.
➡️ February 8, 2026: CrossCurveFi
Damage: ~$3M
What happened: Cross-chain message validation failure. Fake or forged Axelar-style messages were accepted by the receiver contract.
➡️ February 10, 2026: Private user
Damage: ~$118,785
What happened: Malicious approval. The victim signed an increaseAllowance transaction and the attacker drained BUSD.
➡️ February 17, 2026: Private user
Damage: ~$599,714
What happened: Address poisoning. The attacker planted a lookalike address in the transaction history.
➡️ February 18, 2026: Private user
Damage: ~$337,069
What happened: Phishing approval signature. The victim approved USDT spending for a scammer-controlled address.
➡️ February 18, 2026: Private user
Damage: ~$157K
What happened: Address poisoning. Again, a visually similar address, again a wallet drain.
➡️ February 24, 2026: IoTeX / ioTube bridge
Damage: ~$4.4M
What happened: Bridge and private-key failure. Validator/key compromise and unauthorized minting hit the bridge infrastructure.
➡️ February 25, 2026: Private user
Damage: ~$388,051
What happened: Phishing approval. The victim signed away token-spending permission.
➡️ February 26, 2026: YieldBlox
Damage: ~$10.2M
What happened: Oracle and collateral-pricing manipulation. Weak pricing assumptions allowed undercollateralized extraction.
➡️ February 2026: Token vesting phishing campaign
Damage: Not cleanly quantified
What happened: Project administrators were targeted with fake vesting or token-management interfaces designed to redirect allocations and abuse permissions.
➡️ February 2026: South Korean National Tax Service seed-phrase leak
Damage: ~$4.8M
What happened: Operational security failure. A seed phrase was reportedly exposed in a public photograph.
➡️ February 2026: Figure Technology breach
Damage: Not cleanly public
What happened: Infrastructure breach affecting systems connected to blockchain-based financial services.
➡️ February 2026: https://t.co/drXMBRiwRC
Damage: Not cleanly public
What happened: Slow-rug / exit-phase behaviour. User funds were reportedly converted into non-transferable “wallet credits.”
➡️ February 2026: DOJ pig-butchering seizure
Damage: ~$6.1M seized
What happened: Enforcement action against crypto linked to a global investment-fraud network.
➡️ February 2026: Lionsgate Network fraud reports
Damage: ~$45M reported by 180 victims
What happened: Fraud bucket. Victims reported major losses from social-engineered crypto investment scams.
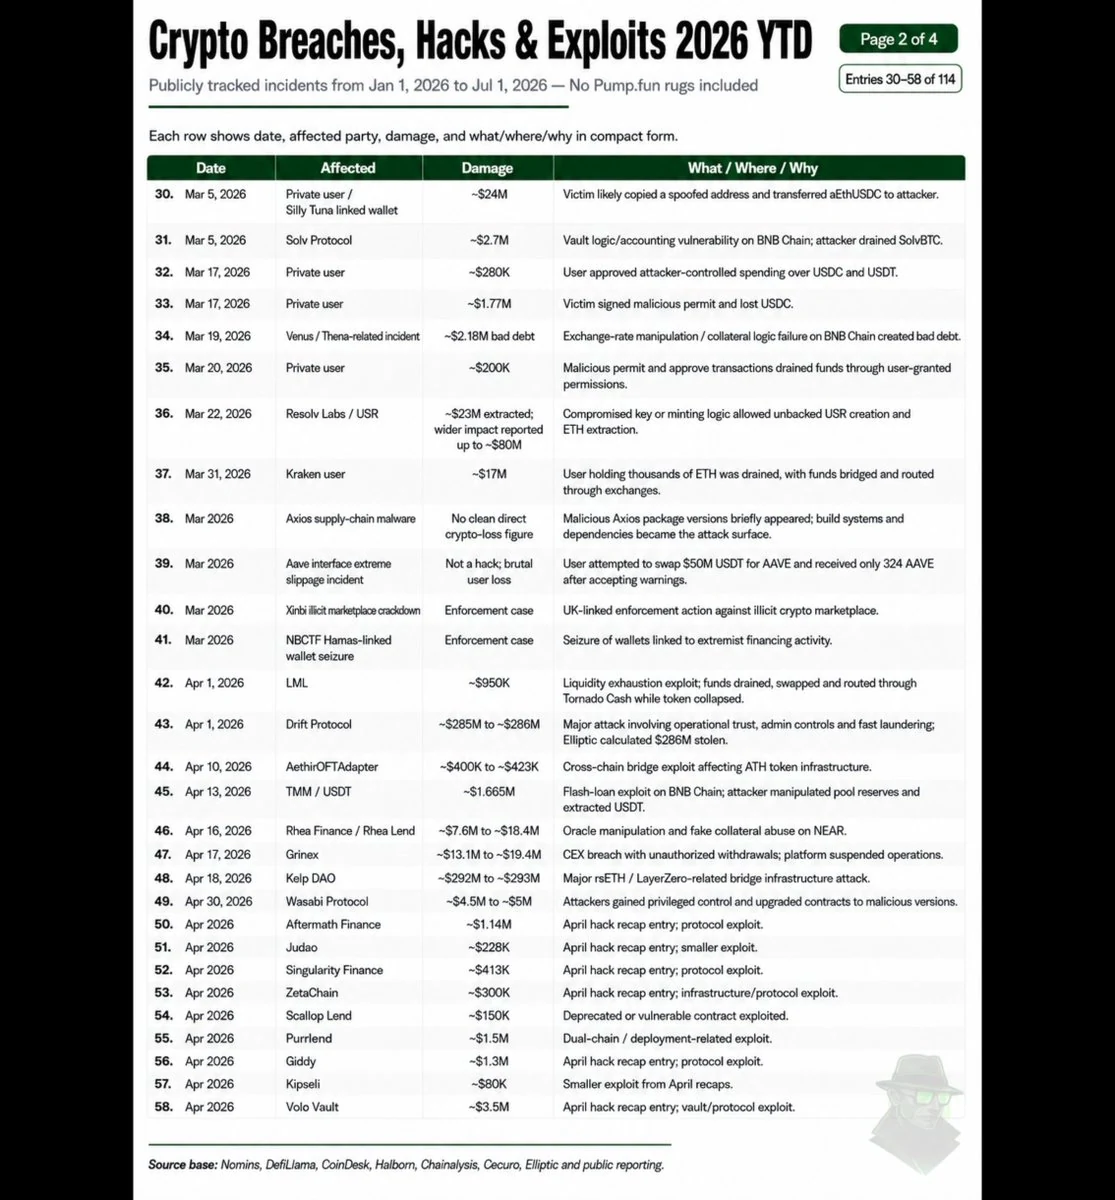
➡️ March 5, 2026: Private user / “Silly Tuna” linked wallet
Damage: ~$24M
What happened: Address poisoning. The victim likely copied a spoofed address and transferred aEthUSDC to the attacker.
➡️ March 5, 2026: Solv Protocol
Damage: ~$2.7M
What happened: Vault logic / accounting vulnerability on BNB Chain. The attacker manipulated internal accounting and drained SolvBTC.
➡️ March 17, 2026: Private user
Damage: ~$280K
What happened: Malicious permit signature. The user approved attacker-controlled spending over USDC and USDT.
➡️ March 17, 2026: Private user
Damage: ~$1.77M
What happened: Phishing approval exploit. The victim signed a malicious permit and lost USDC.
➡️ March 19, 2026: Venus / Thena-related incident
Damage: ~$2.18M bad debt
What happened: Exchange-rate manipulation / collateral logic failure on BNB Chain.
➡️ March 20, 2026: Private user
Damage: ~$200K
What happened: Malicious permit and approve transactions. The attacker drained funds through user-granted permissions.
➡️ March 22, 2026: Resolv Labs / USR
Damage: ~$23M extracted, wider unbacked minting impact reported up to ~$80M
What happened: Stablecoin minting failure. A compromised key or minting logic failure allowed unbacked USR creation and ETH extraction.
➡️ March 31, 2026: Kraken user
Damage: ~$17M
What happened: Social engineering / account compromise. A user holding thousands of ETH was drained, with funds bridged and routed through exchanges.
➡️ March 2026: Axios supply-chain malware
Damage: No clean direct crypto-loss figure
What happened: Developer supply-chain compromise. Malicious Axios package versions briefly appeared, again proving that crypto security also depends on build systems and dependencies.
➡️ March 2026: Aave interface extreme slippage incident
Damage: Not a hack, but a brutal user loss
What happened: A user attempted to swap $50M USDT for AAVE and received only 324 AAVE after accepting warnings. The system worked as designed. That is exactly why it belongs in the scandal list.
➡️ March 2026: Xinbi illicit marketplace crackdown
Damage: Enforcement case, not a protocol hack
What happened: UK-linked enforcement action against an illicit crypto marketplace.
➡️ March 2026: NBCTF Hamas-linked wallet seizure
Damage: Enforcement case, not a protocol hack
What happened: Seizure of wallets linked to extremist financing activity.
➡️ April 1, 2026: LML
Damage: ~$950K
What happened: Liquidity exhaustion exploit. Funds were drained, swapped and routed through Tornado Cash while the token collapsed.
➡️ April 1, 2026: Drift Protocol
Damage: ~$285M
What happened: Social engineering, governance and admin-control failure. One of the biggest attacks of 2026. The protocol was not beaten by a simple bug. It was beaten through operational trust.
➡️ April 10, 2026: AethirOFTAdapter
Damage: ~$400K to ~$423K
What happened: Cross-chain bridge exploit affecting ATH token infrastructure.
➡️ April 13, 2026: TMM / USDT
Damage: ~$1.665M
What happened: Flash-loan exploit on BNB Chain. The attacker manipulated pool reserves and extracted USDT.
➡️ April 16, 2026: Rhea Finance / Rhea Lend
Damage: Reported between ~$7.6M and ~$18.4M depending on tracker
What happened: Oracle manipulation and fake collateral abuse on NEAR.
➡️ April 17, 2026: Grinex
Damage: Reported between ~$13.1M and ~$19.4M
What happened: Centralized exchange breach. Unauthorized withdrawals forced the platform to suspend operations.
➡️ April 18, 2026: Kelp DAO
Damage: ~$292M to ~$293M
What happened: Bridge infrastructure compromise. A major rsETH / LayerZero-related attack and one of the worst bridge failures of the year.
➡️ April 30, 2026: Wasabi Protocol
Damage: ~$4.5M to ~$5M
What happened: Admin-key compromise. Attackers gained privileged control and upgraded contracts to malicious versions.
➡️ April 2026: Aftermath Finance
Damage: ~$1.14M
What happened: April hack recap entry. Protocol exploit.
➡️ April 2026: Judao
Damage: ~$228K
What happened: April hack recap entry. Smaller exploit, same broken-security background noise.
➡️ April 2026: Singularity Finance
Damage: ~$413K
What happened: April hack recap entry. Protocol exploit.
➡️ April 2026: ZetaChain
Damage: ~$300K
What happened: April hack recap entry. Infrastructure/protocol exploit.
➡️ April 2026: Scallop Lend
Damage: ~$150K
What happened: Deprecated or vulnerable contract exploit. “Deprecated” does not mean safe when contracts remain live.
➡️ April 2026: Purrlend
Damage: ~$1.5M
What happened: Dual-chain / deployment-related exploit. Same code, new chain, fresh attack surface.
➡️ April 2026: Giddy
Damage: ~$1.3M
What happened: April hack recap entry. Protocol exploit.
➡️ April 2026: Kipseli
Damage: ~$80K
What happened: Smaller exploit. Still part of April’s near-daily exploit cadence.
➡️ April 2026: Volo Vault
Damage: ~$3.5M
What happened: April hack recap entry. Vault/protocol exploit.
➡️ April 2026: Thetanuts Finance
Damage: ~$50K
What happened: Smaller protocol exploit reported in April recaps.
➡️ April 2026: Juicebox V3
Damage: ~$52K
What happened: Smaller smart contract exploit.
➡️ April 2026: Zerion Wallet
Damage: ~$100K
What happened: Wallet/security incident tied to credential or infrastructure compromise reporting.
➡️ April 2026: MONA
Damage: ~$60.95K
What happened: Smaller exploit entry.
➡️ April 2026: Dango
Damage: ~$410K
What happened: Smaller exploit entry.
➡️ April 2026: SubQuery Network
Damage: ~$60K
What happened: Smaller exploit entry.
➡️ April 2026: Hyperbridge
Damage: ~$2.5M
What happened: Bridge proof-verification / cross-chain message failure.
➡️ April 2026: Silo V2
Damage: ~$392K
What happened: Protocol exploit reported in April recaps.
➡️ April 2026: CoW Swap
Damage: Not cleanly public in the recap
What happened: Domain / frontend / supply-chain security issue. The user-facing layer became the attack surface.
➡️ April 2026: Vercel breach
Damage: Not a direct DeFi drain, but major ecosystem exposure
What happened: Third-party AI/tooling compromise exposed API keys, GitHub tokens and NPM tokens. Web3 teams relying on hosted frontends had to rotate secrets.
➡️ April 2026: Sweat Economy
Damage: Not cleanly public in the source set
What happened: Reported April incident involving rapid token supply impact. Another example of token infrastructure collapsing under bad assumptions.
➡️ April 2026: April phishing bucket
Damage: ~$3.5M additional phishing losses in some recaps
What happened: User-level wallet drains and phishing cases sitting beside the protocol hacks.
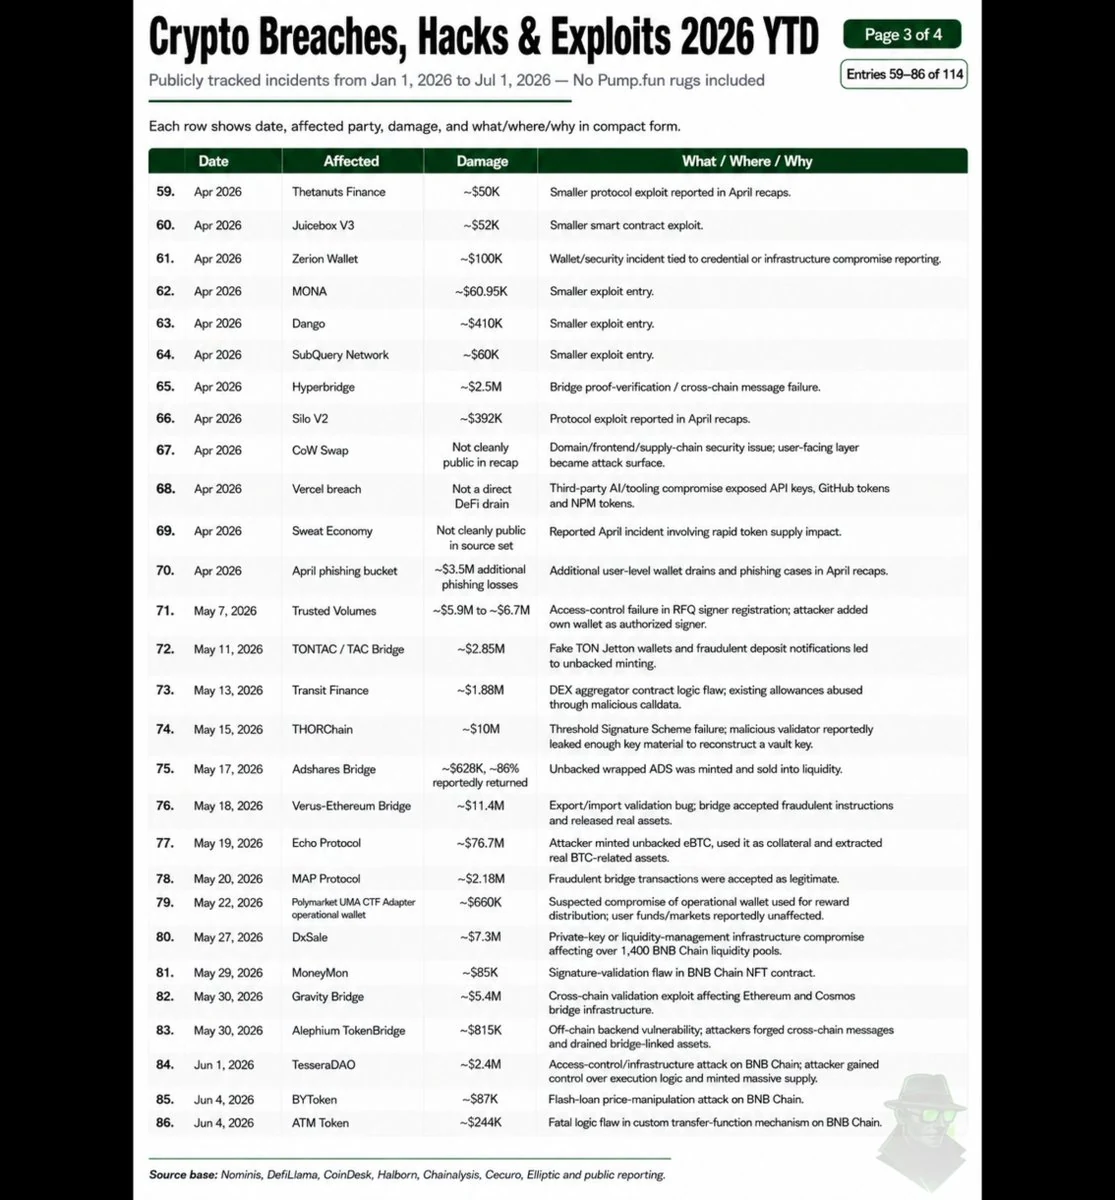
➡️ May 7, 2026: Trusted Volumes
Damage: ~$5.9M to ~$6.7M
What happened: Access-control failure in RFQ signer registration. The attacker added their own wallet as an authorized signer.
➡️ May 11, 2026: TONTAC / TAC Bridge
Damage: ~$2.85M
What happened: Bridge verification failure. Fake TON Jetton wallets and fraudulent deposit notifications led to unbacked minting.
➡️ May 13, 2026: Transit Finance
Damage: ~$1.88M
What happened: DEX aggregator contract logic flaw. Existing allowances were abused through malicious calldata.
➡️ May 15, 2026: THORChain
Damage: ~$10M
What happened: Threshold Signature Scheme failure. A malicious validator reportedly leaked enough key material to reconstruct a vault key.
➡️ May 17, 2026: Adshares Bridge
Damage: ~$628K, about 86% reportedly returned
What happened: Bridge proof-verification failure. Unbacked wrapped ADS was minted and sold into liquidity.
➡️ May 18, 2026: Verus-Ethereum Bridge
Damage: ~$11.4M
What happened: Cross-chain export/import validation bug. The bridge accepted fraudulent instructions and released real assets.
➡️ May 19, 2026: Echo Protocol
Damage: ~$76.7M
What happened: Admin-key compromise. The attacker minted unbacked eBTC, used it as collateral and extracted real BTC-related assets.
➡️ May 20, 2026: MAP Protocol
Damage: ~$2.18M
What happened: Cross-chain message verification exploit. Fraudulent bridge transactions were accepted as legitimate.
➡️ May 22, 2026: Polymarket UMA CTF Adapter operational wallet
Damage: ~$660K
What happened: Suspected private-key compromise of an operational wallet used for reward distribution. Polymarket said user funds and markets were not affected.
➡️ May 27, 2026: DxSale
Damage: ~$7.3M
What happened: Private-key or liquidity-management infrastructure compromise. More than 1,400 BNB Chain liquidity pools were reportedly affected.
➡️ May 29, 2026: MoneyMon
Damage: ~$85K
What happened: Signature-validation flaw in a BNB Chain NFT contract.
➡️ May 30, 2026: Gravity Bridge
Damage: ~$5.4M
What happened: Cross-chain validation exploit affecting Ethereum and Cosmos bridge infrastructure.
➡️ May 30, 2026: Alephium TokenBridge
Damage: ~$815K
What happened: Off-chain backend vulnerability. Attackers forged cross-chain messages and drained bridge-linked assets.
➡️ June 1, 2026: TesseraDAO
Damage: ~$2.4M
What happened: Access-control / infrastructure attack on BNB Chain. The attacker gained control over execution logic and minted massive token supply.
➡️ June 4, 2026: BYToken
Damage: ~$87K
What happened: Flash-loan price-manipulation attack on BNB Chain.
➡️ June 4, 2026: ATM Token
Damage: ~$244K
What happened: Fatal logic flaw in a custom transfer-function mechanism on BNB Chain.
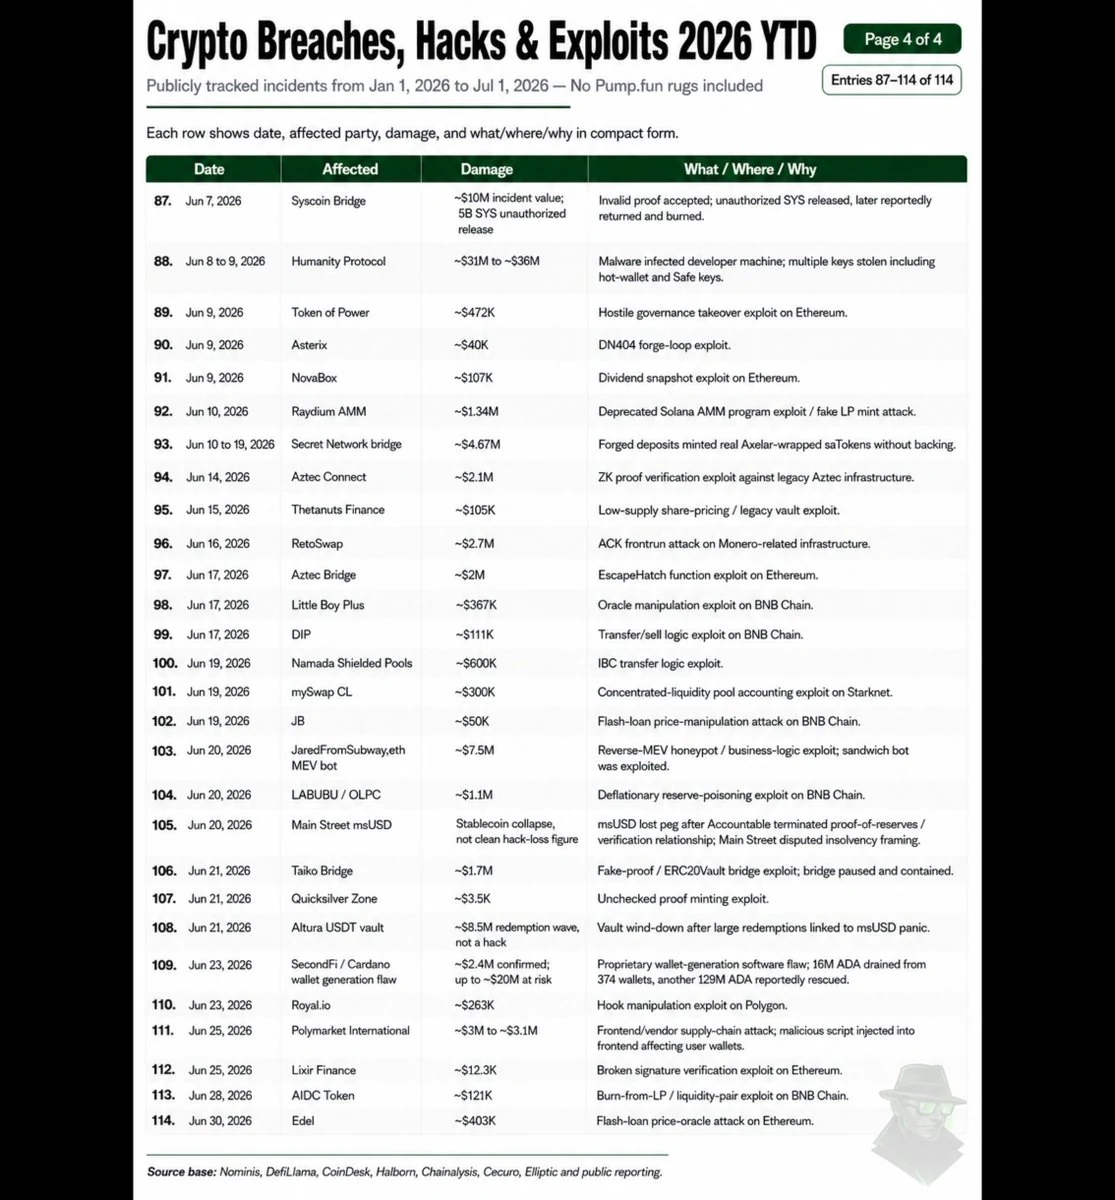
➡️ June 7, 2026: Syscoin Bridge
Damage: ~$10M incident value, 5B SYS unauthorized release
What happened: Bridge proof-validation failure. Invalid proof accepted, unauthorized SYS released, funds later reportedly returned and burned.
➡️ June 8 to 9, 2026: Humanity Protocol
Damage: ~$31M to ~$36M
What happened: Private-key compromise after malware infected a developer machine. Multiple keys were stolen, including hot-wallet and Safe keys.
➡️ June 9, 2026: Token of Power
Damage: ~$472K
What happened: Hostile governance takeover exploit on Ethereum.
➡️ June 9, 2026: Asterix
Damage: ~$40K
What happened: DN404 forge-loop exploit.
➡️ June 9, 2026: NovaBox
Damage: ~$107K
What happened: Dividend snapshot exploit on Ethereum.
➡️ June 10, 2026: Raydium AMM
Damage: ~$1.34M
What happened: Deprecated Solana AMM program exploit / fake LP mint attack.
➡️ June 10 to 19, 2026: Secret Network bridge
Damage: ~$4.67M
What happened: Infinite mint / unbacked saToken bug. Forged deposits minted real Axelar-wrapped saTokens without backing.
➡️ June 14, 2026: Aztec Connect
Damage: ~$2.1M
What happened: ZK proof verification exploit against legacy Aztec infrastructure.
➡️ June 15, 2026: Thetanuts Finance
Damage: ~$105K
What happened: Low-supply share-pricing / legacy vault exploit.
➡️ June 16, 2026: RetoSwap
Damage: ~$2.7M
What happened: ACK frontrun attack on Monero-related infrastructure.
➡️ June 17, 2026: Aztec Bridge
Damage: ~$2M
What happened: EscapeHatch function exploit on Ethereum.
➡️ June 17, 2026: Little Boy Plus
Damage: ~$367K
What happened: Oracle manipulation exploit on BNB Chain.
➡️ June 17, 2026: DIP
Damage: ~$111K
What happened: Transfer/sell logic exploit on BNB Chain.
➡️ June 19, 2026: Namada Shielded Pools
Damage: ~$600K
What happened: IBC transfer logic exploit.
➡️ June 19, 2026: mySwap CL
Damage: ~$300K
What happened: Concentrated-liquidity pool accounting exploit on Starknet.
➡️ June 19, 2026: JB
Damage: ~$50K
What happened: Flash-loan price-manipulation attack on BNB Chain.
➡️ June 20, 2026: JaredFromSubway.eth MEV bot
Damage: ~$7.5M
What happened: Reverse-MEV honeypot / business-logic exploit. Even the sandwich bot got eaten.
➡️ June 20, 2026: LABUBU / OLPC
Damage: ~$1.1M
What happened: Deflationary reserve-poisoning exploit on BNB Chain.
➡️ June 20, 2026: Main Street msUSD
Damage: Stablecoin collapse, not a clean hack-loss figure
What happened: msUSD lost its peg after Accountable terminated its proof-of-reserves / verification relationship. Main Street said it was a reporting infrastructure issue, not insolvency. Either way, confidence died first.
➡️ June 21, 2026: Taiko Bridge
Damage: ~$1.7M
What happened: Fake-proof / ERC20Vault bridge exploit. The bridge was paused and contained.
➡️ June 21, 2026: Quicksilver Zone
Damage: ~$3.5K
What happened: Unchecked proof minting exploit.
➡️ June 21, 2026: Altura USDT vault
Damage: ~$8.5M redemption wave, not a hack
What happened: Confidence run linked to msUSD panic. Redemptions forced a vault wind-down.
➡️ June 23, 2026: SecondFi / Cardano wallet generation flaw
Damage: ~$2.4M confirmed, up to ~$20M at risk
What happened: Proprietary wallet-generation software flaw. 16M ADA drained from 374 wallets, while another 129M ADA was reportedly rescued before attackers reached it.
➡️ June 23, 2026: https://t.co/QhvhmR3dbU
Damage: ~$263K
What happened: Hook manipulation exploit on Polygon.
➡️ June 25, 2026: Polymarket International
Damage: ~$3M to ~$3.1M
What happened: Frontend / third-party vendor supply-chain attack. Malicious script injected into the frontend, affecting user wallets.
➡️ June 25, 2026: Lixir Finance
Damage: ~$12.3K
What happened: Broken signature verification exploit on Ethereum.
➡️ June 28, 2026: AIDC Token
Damage: ~$121K in some tracker summaries
What happened: Burn-from-LP / liquidity-pair exploit on BNB Chain.
➡️ June 30, 2026: Edel
Damage: ~$403K
What happened: Flash-loan price-oracle attack on Ethereum.
By July 1, 2026, this industry has already produced a full half-year crime scene: bridge failures, admin-key failures, private-key failures, oracle failures, frontend failures, fake collateral, unbacked minting, malicious approvals, poisoned dependencies, stablecoin confidence runs and millions of dead memecoins.
As I said, the dark figure is much higher.
The smaller scams that never even reach my desk probably add at least the same amount again, in my estimate.
And that still does not include money quietly withheld, hidden, mismanaged or extracted by CEXs and other centralized actors.
It is fucking sad, but at this point I honestly believe we need regulation.
thoughts?