钓鱼攻击、漏洞与隐私
DragonForce and the ransomware service economy
An account of the DragonForce ecosystem, its affiliate model and the business structure around ransomware.
 MASTR
首次发表 6 min · 1,229 词
Original publication · 1 Oct 2025. Figures, claims and opinions reflect the original publication date.
原文为英语,导航提供七种语言。
Originally published as “Meet Dragonforce; ransomware-as-a-service”
I am $MASTR and I monitor the group professionally. I find DragonForce the most interesting group of all, interesting in a forensic and analytical sense and not admirable.
They move like a shadow across whole organisations, striking not for headlines but for maximum chaos. DragonForce hunts the brittle seams of trust between suppliers and customers ambushes the forgotten admin console and turns a single stolen credential into a regional outage. Their attacks are surgical and theatrical at once: silent foothold by day catastrophic encryption by night and a polished leak site to amplify the pain. Forensic traces are cleaned or misdirected leaving investigators to chase ghosts while operations grind to a halt. I find them fascinating not because they are admirable but because their mix of tradecraft theatre and supply chain brutality reveals the true fragility of our digital infrastructure.
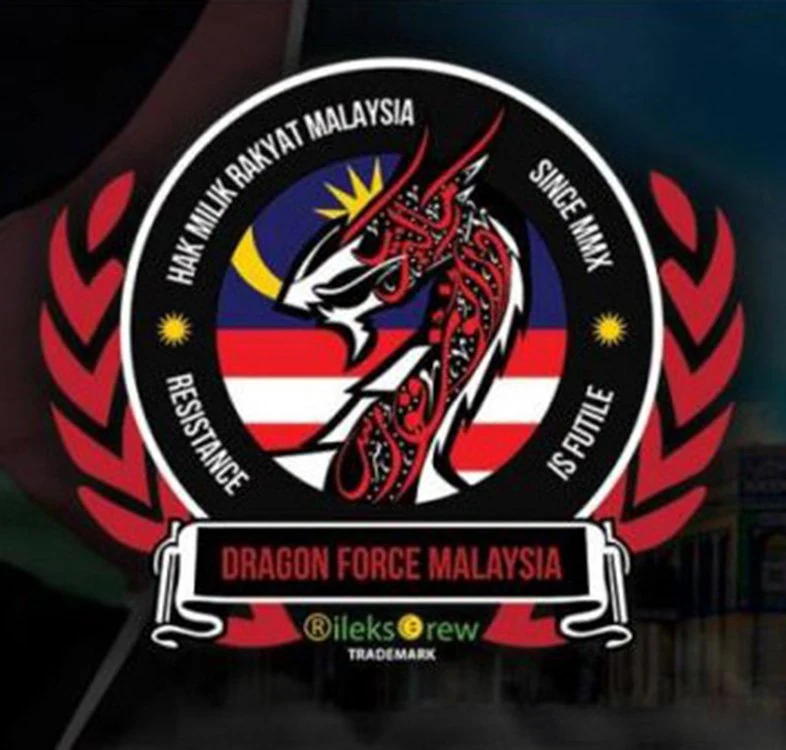
DragonForce did not emerge fully formed.
At first they sounded like loud online activists, a crew calling themselves DragonForce Malaysia and staging noisy campaigns that drew attention but little lasting harm.
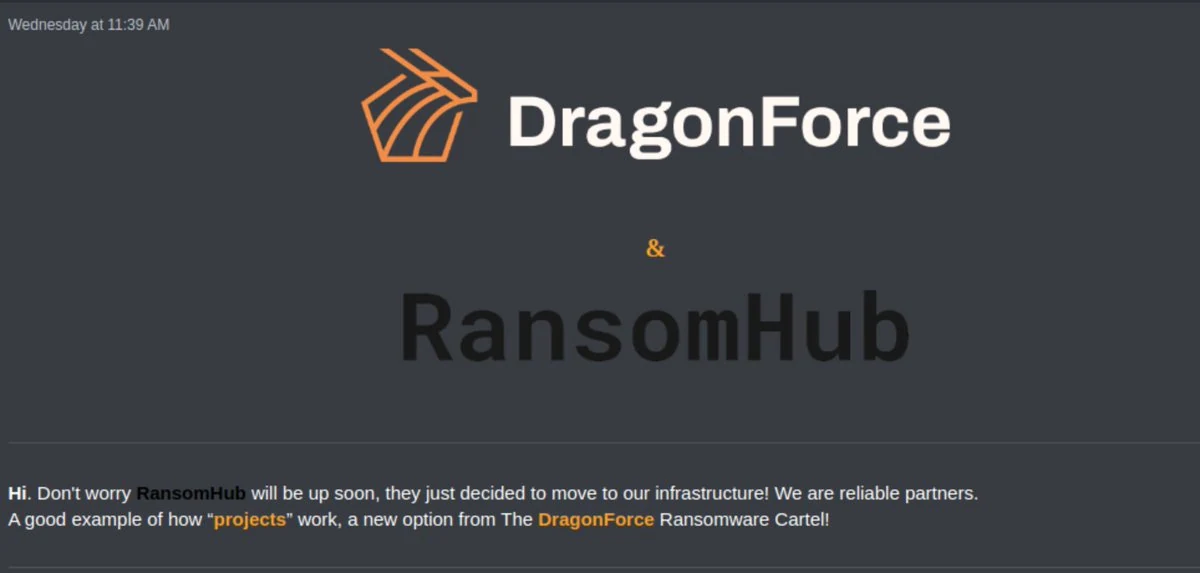
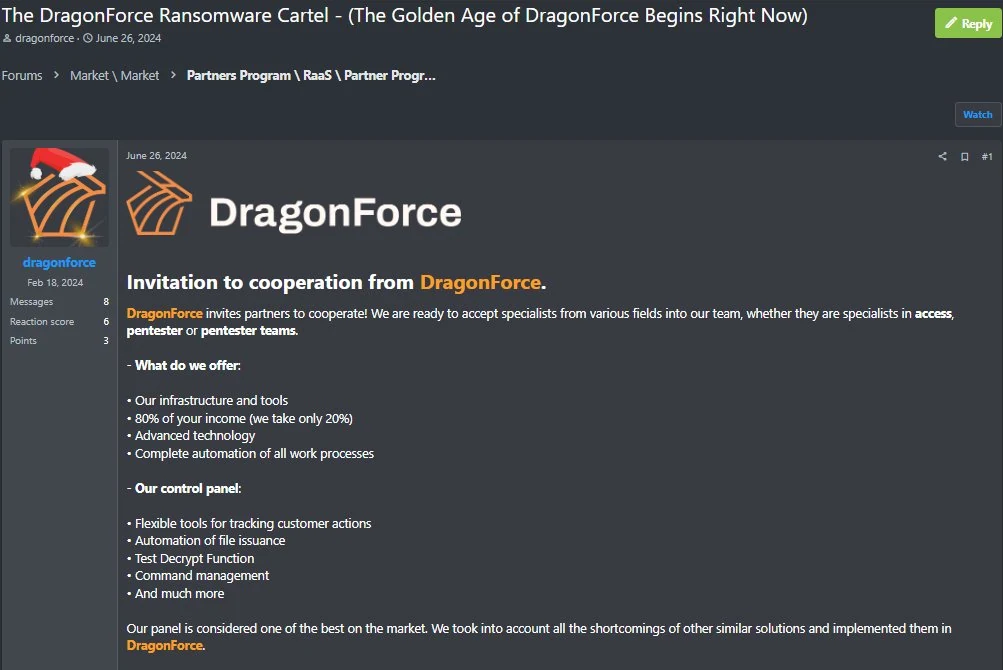
Over time their mask slipped. By late 2023 the group reappeared with a new face and a new agenda. They stopped posing as street fighters of the internet and began to operate like a franchise. They sell access to a toolkit, maintain polished leak sites and teach affiliates how to run high yield extortion operations. The crown jewel of their business model is Ransomware as a Service. Affiliates rent the tools, customise payloads, pick targets and keep the bulk of any ransom payments while DragonForce takes a cut. It is organised crime packaged as software.
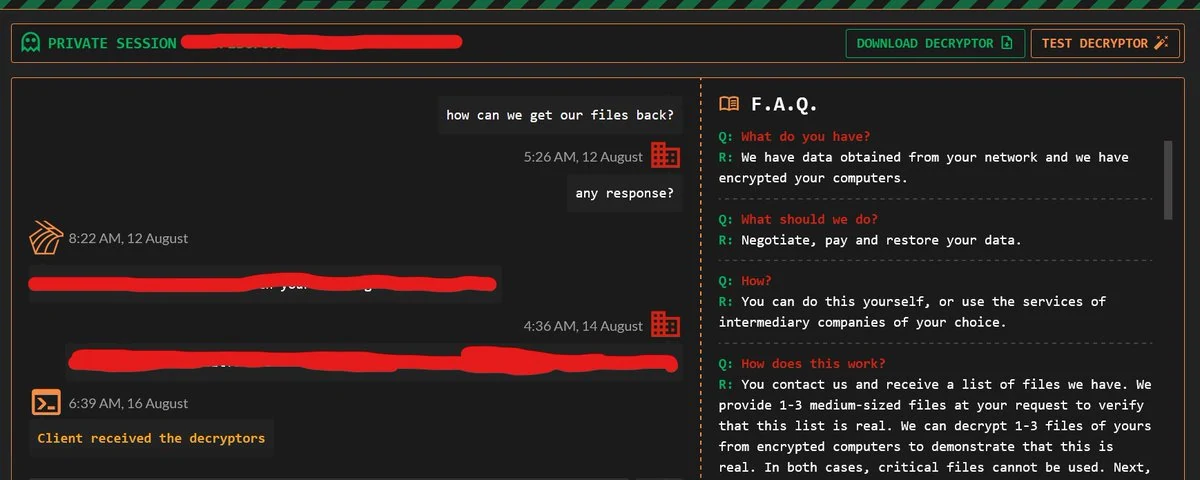
Their method is chillingly simple and brutally effective. They find a way in using stolen VPN credentials, weak remote desktop passwords, social engineering or by exploiting vulnerabilities in remote management software. Once inside they move fast. They steal data, often years of customer records, financial ledgers and internal communications. Then they lock systems with encryption and make a demand for payment in crypto. If the victim refuses the stolen files appear on a leak site on the dark web. The threat to publish private data forces organisations into impossible choices. Technically they use tools such as Cobalt Strike, #Mimikatz and #SystemBC and sometimes bring your own vulnerable driver techniques to blunt endpoint protections. They tidy up logs and cover traces.
Below is a comprehensive, curated listing of known victims and impacted organisations compiled from open cyber intelligence records and reporting.
This list groups representative victims by region and sector and is long because the group has many targets. For a live, searchable catalogue with dozens and in some sources hundreds of entries see the full tracker at Ransomware.live which records 200 plus victims and is updated continuously.
Notable victims and impacted organisations attributed to DragonForce or appearing on public leak trackers and reporting;
United Kingdom and Western Europe
- Marks and Spencer UK retail
- Co op UK retail
- Harrods UK luxury retail
- Harrods related supplier and third party systems affected in multiple incidents
- Accuracy International UK defence manufacturer
- Hardings Transport logistics UK
- Fullington Trailways transport US but listed in trackers due to cross border impact via MSP compromise
United States and North America
- JCC Rockland community organisation
- Johnstone Supply Dallas Fort Worth industrial supply
- Mastery Schools education
- Asheville Eye Associates healthcare
- Williams Tank Lines transport and logistics
- Engineered Tower Solutions telecom engineering
- Orbit Software software vendor
Asia Pacific and Middle East
- PT PINS Indonesia IoT subsidiary and service provider
- FINN mobility services in Australia
Industry spread and smaller victims tracked globally
- Construction firms and suppliers in Italy, Brazil and the Netherlands
- Pharma contract manufacturers and lab services
- Manufacturing firms including plastics parts and tooling suppliers
- Local government entities and regional municipalities
- Managed Service Providers and IT consultancies that became pivot points for supply chain compromise
Expanded sample list drawn from open trackers and security reports. This is not a closed list. Public trackers list many more companies across Americas Europe Asia and Oceania. For the full crawlable list, including discovery dates and leak pages, consult Ransomware.live and related threat intelligence feeds. These sources show dozens to hundreds of unique victim entries across 2023 to 2025 and continue to be updated.
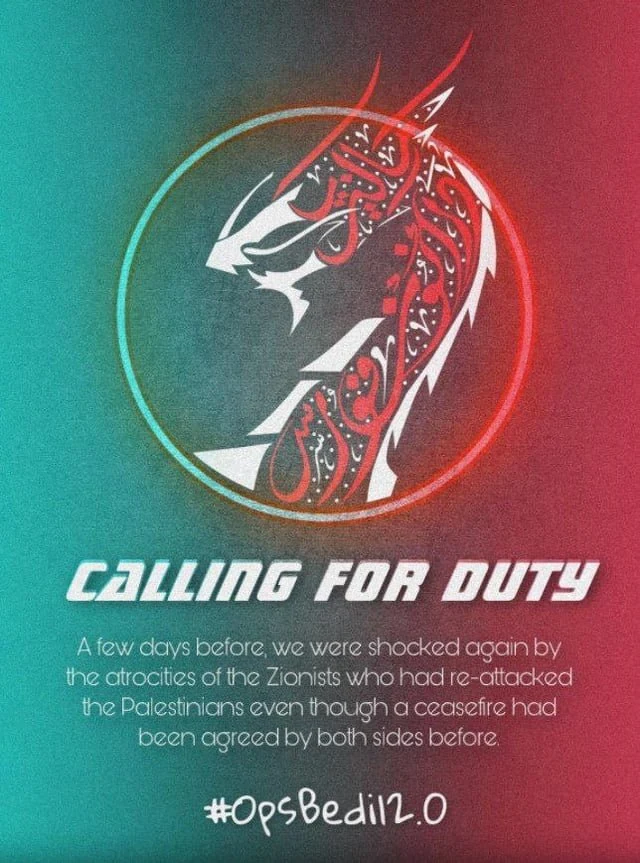
At first DragonForce presented itself with a hacktivist tone. Early activity attributed to the name included politically charged messaging and noisy campaigns associated with Malaysian regional activism and with pro Palestinian themed stunts. That early posture created confusion when the group later pivoted sharply toward profit driven extortion.
By late 2023 and into 2024 the evidence shows a clear shift toward criminal RaaS operations and commercial extortion. Public reporting from multiple security firms documents the affiliate model the professional leak infrastructure and the explicit ransom demands. The political cover story appears to have been replaced or supplemented by a business model built on multi extortion. That means operationally they now act like criminals first and ideological actors second or not at all.
Some incidents still carry political messaging in kill notes or in early campaigns. However the majority of high impact breaches and subsequent leak postings are pure extortion with monetary demands. That pattern suggests opportunistic targeting rather than sustained ideologically driven campaigns. In short they have hacktivist roots but their recent behaviour is dominated by monetisation.
Like many prolific ransomware groups #DragonForce reportedly avoids attacking targets in Russia and certain former Soviet states. That behavioural pattern does not prove state sponsorship but it does indicate an operating environment where attacking some geographies is taboo. Analysts treat that as an indication of where the operators feel protected.
Crypto unlocked new possibilities for value and for anonymity. Those same properties created pathways for groups like DragonForce to convert stolen data into cash and power. Understanding the mechanics, the incentives and the human impact is the only way to imagine responses or to craft believable fictional arcs.
DragonForce represents more than a gang of criminals. They are a mirror of our digital age, an age where information can be stolen, weaponised and sold in minutes.
Their operations reveal the fragility of global infrastructure and the high cost of ignoring weak points. Every encrypted server, every leaked database and every silenced victim testifies to the scale of the threat.
They also show how crime has become theatre. A polished leak site is not just extortion, it is performance. Each posting is designed to humiliate, to pressure, to spread fear. Victims are not just paying for silence, they are paying to stay out of the spotlight of a global stage.
And still, behind the spectacle, the consequences are brutally human. Patients waiting for treatment, students locked out of classrooms, workers stranded when logistics chains collapse. For DragonForce, these are numbers in a wallet. For the rest of the world, they are lives disrupted and trust destroyed.
What makes them the most interesting to analyse is not admiration but the complexity of their methods and the clarity with which they expose weaknesses that most organisations pretend do not exist. #DragonForce proves that one stolen credential can become an international crisis, that one overlooked patch can trigger millions in damage, and that one criminal franchise can shake entire sectors of the economy.
This is why studying them matters. Because every headline is only the surface. Because every payment fuels the cycle. And because the next attack will always come.
- $MASTR
Thank you for following and supporting the mission of $MASTR.