

MASTR · CRYPTO & WEB3
Bridges: a message, a verifier and a claim on another chain
Moving an asset across chains usually creates dependencies between two state machines. Follow the verifier and the redemption route.
Les chapitres et schémas techniques sont en anglais. La navigation existe en sept langues.
What convinces the destination chain that the source event really happened?
The asset does not physically travel
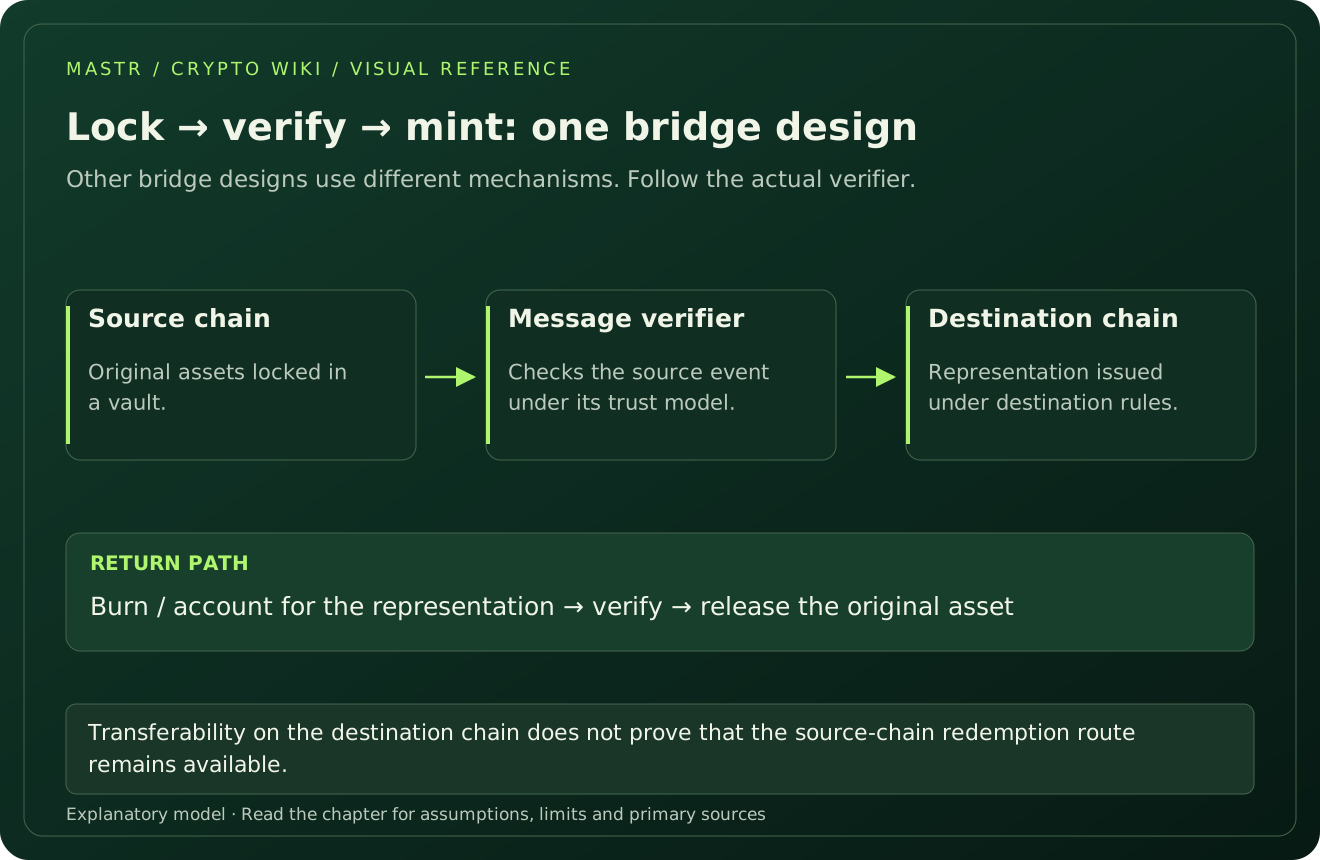
In a common lock-and-mint design, assets are held on one chain and a representation is issued on another. A return transfer burns or otherwise accounts for the representation before the original assets are released. Other bridges use liquidity providers or issuer-controlled burn-and-mint mechanisms. Calling all of them a transfer hides their different claims and dependencies. Start by naming the actual design.
The verifier is the central question
The destination needs a reason to accept a message about the source chain. It may rely on a set of signers, a light client, proofs, a challenge process or a combination. Count independent control domains, not only keys displayed in a threshold. Several signers operated by the same organisation or relying on the same infrastructure may share failure modes. An upgrade administrator can also change the system after the initial review.
Finality must cross the boundary
A source transaction that later disappears in a reorganisation can leave a destination claim unsupported if the bridge accepted it too early. A bridge therefore needs explicit rules for source finality and message uniqueness. Replay protection matters because the same valid message must not produce repeated releases. Chain identifiers, nonce handling and the interpretation of the source event are part of the security boundary.
Wrapped assets can carry a local discount
A representation may continue to trade after its backing or withdrawal path is impaired. Its ticker can resemble the original asset even when redemption has changed. Lending protocols accepting it inherit that dependency. Several versions of an asset on the same chain can have different issuers or bridges. The canonical label in a user interface is not a substitute for checking the contract and its actual backing.
Evaluate failure and exit
Ask what happens if the signers stop, the source chain halts, an administrator pauses the bridge or the verifier is upgraded. A route may be secure against theft but unavailable during stress; another may be fast but depend heavily on an operator. Fees and speed are only part of the comparison. The user ultimately needs to know who can authorise a claim and under which conditions it can be redeemed.
Exemple expliqué
A token called bridged ETH can remain transferable on chain B while the vault on chain A is paused. Transferability on B does not prove redeemability on A. The diagram shows that dependency without implying that every bridge uses the same design.
Questions à retenir
- Name the verifier.
- Check source finality and replay protection.
- Trace the exact token’s redemption route.