

MASTR · CRYPTO & WEB3
Before Bitcoin: privacy, digital cash and the missing agreement
The history begins with several different problems: private payments, costly computation, ownership and agreement about what was already spent.
Les chapitres et schémas techniques sont en anglais. La navigation existe en sept langues.
What did Bitcoin combine that its predecessors treated separately?
Start with the problem, not the coin
Digital information is easy to copy. A payment system needs a way to distinguish an authorised transfer from a second attempt to spend the same value. A private payment system also asks a different question: how much should the issuer, recipient or public learn about the payer? These are separate design problems. Solving one does not automatically solve the other. Reading early digital-cash proposals through these questions is more useful than treating them as unfinished versions of today’s tokens.
Privacy was an engineering objective
Eric Hughes’s 1993 Cypherpunk’s Manifesto describes privacy as the ability to choose what to disclose. Its programme connects cryptography with the construction of working systems. The historical distinction matters: the cypherpunk objective was not simply a publicly readable ledger with a token attached. Digital signatures can authenticate a message while revealing a persistent identifier. Encryption can hide content while leaving timing and counterparties visible. A system can decentralise publication and still expose its users.
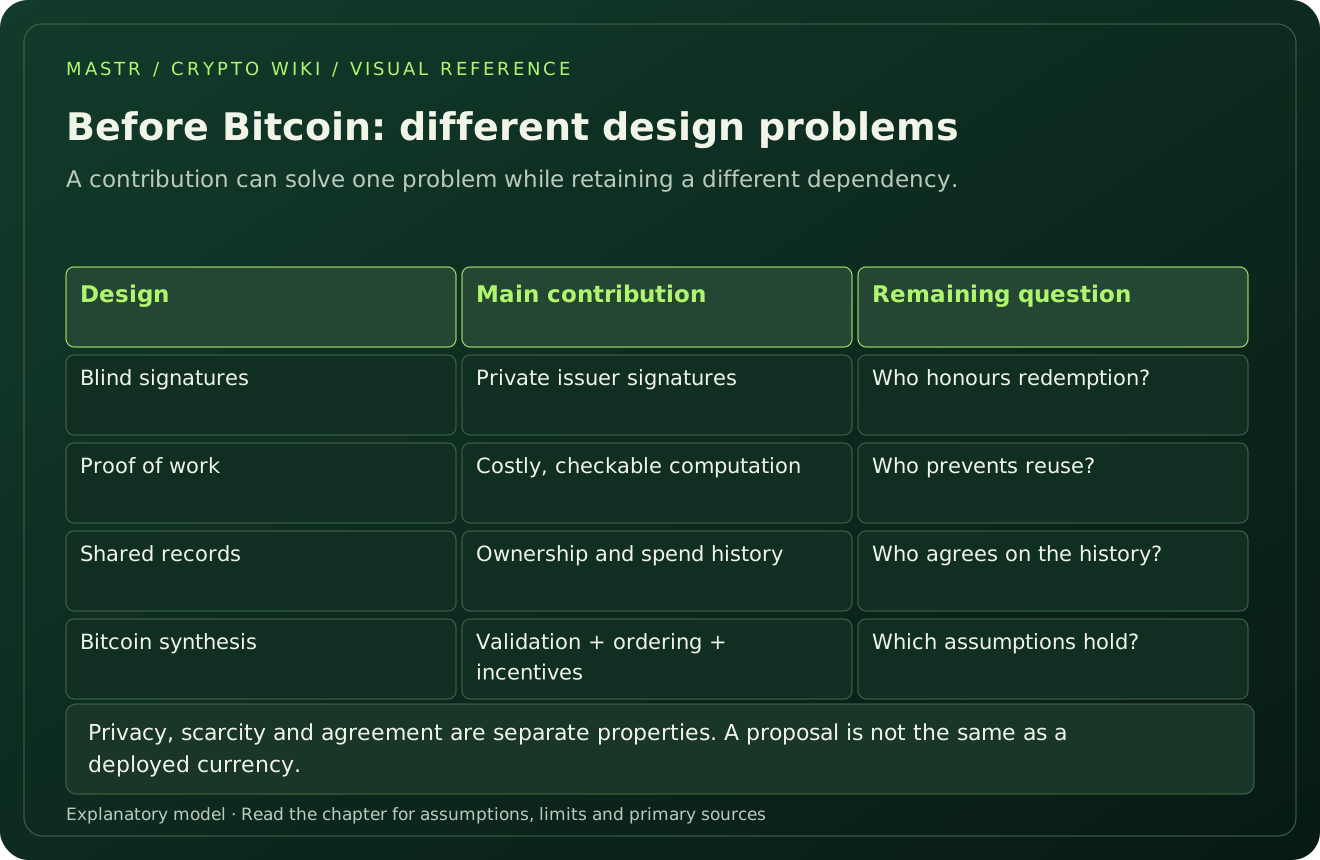
Different predecessors, different trust boundaries
Chaum’s blind-signature work developed a way for an issuer to sign a payment token without learning its unblinded form. It still depended on an issuer. Hashcash made a sender perform computational work, originally as a defence against abuse; it was not itself a complete currency. Wei Dai’s b-money explored shared balances and contracts among pseudonymous participants. Nick Szabo’s bit gold linked costly proofs, timestamps and a property registry, while identifying problems with valuation and the distribution of trust. Hal Finney’s RPOW made work tokens reusable through an attested server. Each contribution changes a specific boundary; none should be credited with a property it did not implement.
Bitcoin’s synthesis
The 2008 Bitcoin paper connects signatures, a public transaction history, proof of work, a rule for choosing between competing histories and an incentive for producing blocks. Its central contribution is a practical way for an open network to order spends without a conventional payment operator. The system does not make copying data impossible. It makes competing claims about spend order subject to shared verification and a cumulative-work rule. Nor does it prove the real identity of an address owner.
How to read this history critically
Separate a proposal’s publication date from the date a working system launched. Distinguish an idea’s influence from a claim that one person invented every ingredient. Avoid using a later market price to judge an earlier research contribution. Ask what the system verifies, who can refuse service, which party can create money, and what happens when two valid-looking spends conflict. These questions remain useful for stablecoins, bridges and rollups, even when their branding sounds very different.
Exemple expliqué
Compare two receipts. A bank-signed token can prove that an issuer authorised value, but redemption depends on that issuer. A Bitcoin output can be checked against the node’s accepted chain, but the user still depends on software, key control and network assumptions. The word “digital” does not make the two receipts equivalent.
Questions à retenir
- Identify the issuer, if there is one.
- Separate privacy from consensus.
- Ask how the design prevents a second spend.