钓鱼攻击、漏洞与隐私
North Korea-linked theft and the first-half 2026 record
They are organised, patient, funded, technically serious and fully aware that crypto still runs on weak humans, lazy security, rushed integrations and teams that spend more on marketing than on infrastructure hardening.
 MASTR
首次发表 2 min · 329 词
Original publication · 9 Jul 2026. Figures, claims and opinions reflect the original publication date.
原文为英语,导航提供七种语言。
01
查看 X 原帖 ↗North Korea-linked hackers stole around $643M (++) in crypto in H1 2026.
Or: "Web3 is unintentionally financing North Korea"
This space has become one of the most profitable funding rails for state-backed cybercrime.
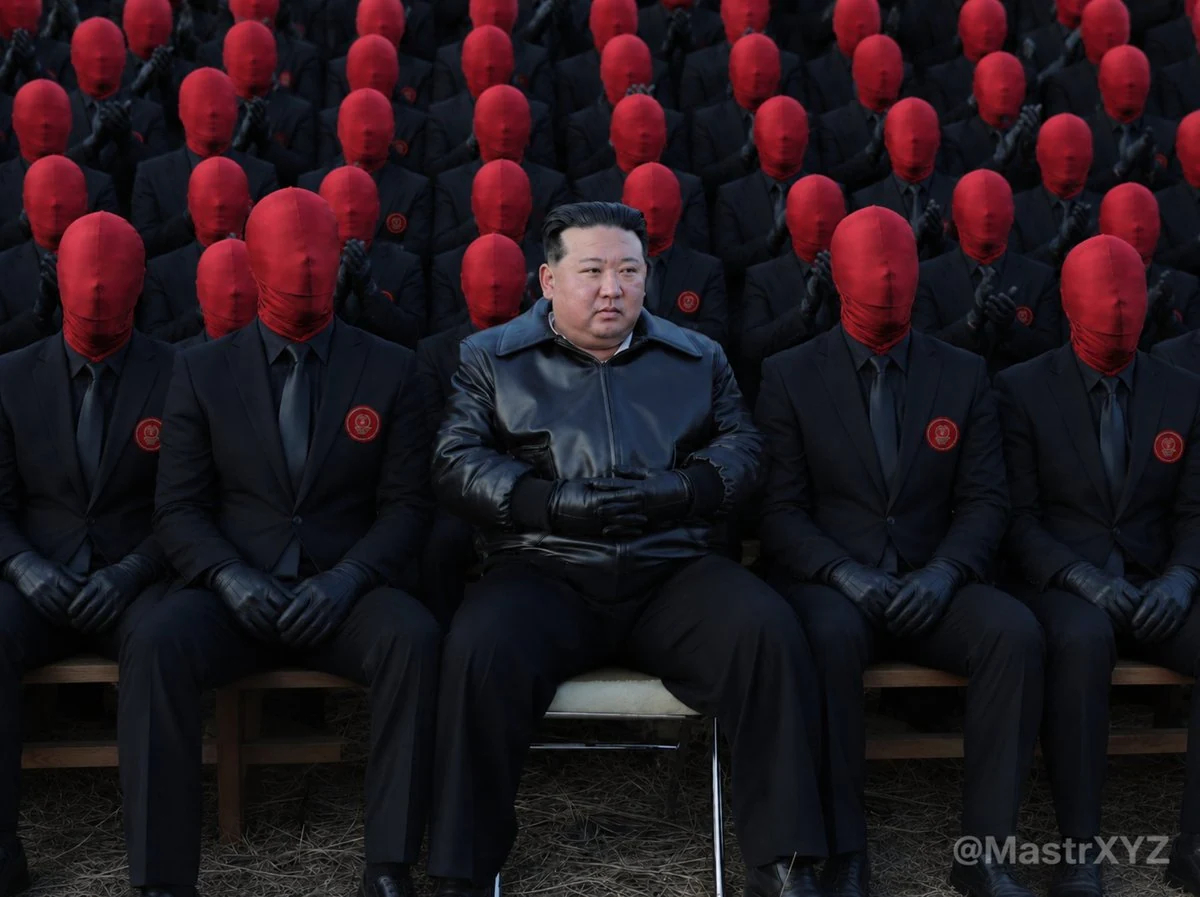
Lazarus and related DPRK-linked groups are not random Telegram scammers with fake Raydium links.
They are organised, patient, funded, technically serious and fully aware that crypto still runs on weak humans, lazy security, rushed integrations and teams that spend more on marketing than on infrastructure hardening.
Two attacks alone explain most of the damage:
Drift and KelpDAO, roughly $577M combined.
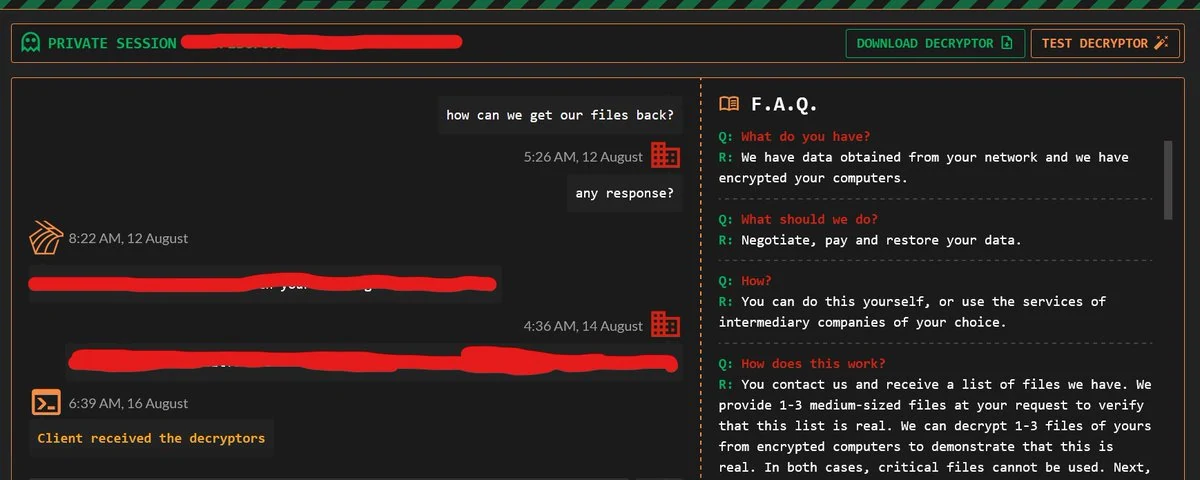
It means one compromised system, one bad verifier setup, one poisoned dependency, one employee laptop, one fake job interview, one malicious attachment, one lazy key-management decision can become a nation-state payday.
The hack usually does not start onchain.
It starts in your hiring process, your Discord DMs, your npm packages, your remote developers, your fake contractors, your browser extensions, your cloud keys, your SSH credentials, your laptop, your Slack, your ego and your assumption that “we are too small to be targeted”.
North Korean operations are moving through DeFi, supply chains, open-source packages, fake developer tools, compromised maintainer accounts, phishing, signed malware and suspected IT-worker infiltration.
This is no longer only about draining hot wallets. It is about getting inside the people and systems that control them.
So when projects spend months farming attention, buying KOL noise, pushing TVL screenshots and pretending an audit badge is a force field, remember this:
....attackers do not care about your brand deck. They care about your weakest operational habit.
Retail loses when protocols treat security as paperwork. Builders lose. The entire space loses when stolen funds keep turning into geopolitical fuel.
Crypto does not only need better contracts.
It needs better minds,
better processes, better access control, better key management, better dependency hygiene, better monitoring.
The next “exploit” may already be sitting in someone’s inbox, pretending to be a recruiter, a developer, a package update, a partner, a KOL.