

Noms, identité et contenu web
DNSSEC and HTTPS: two checks behind a wallet website
Authenticated name resolution and encrypted transport do not certify a financial application.
Les articles et schémas techniques sont en anglais. La navigation est disponible en 7 langues.
Guides de référence
Two separate layers
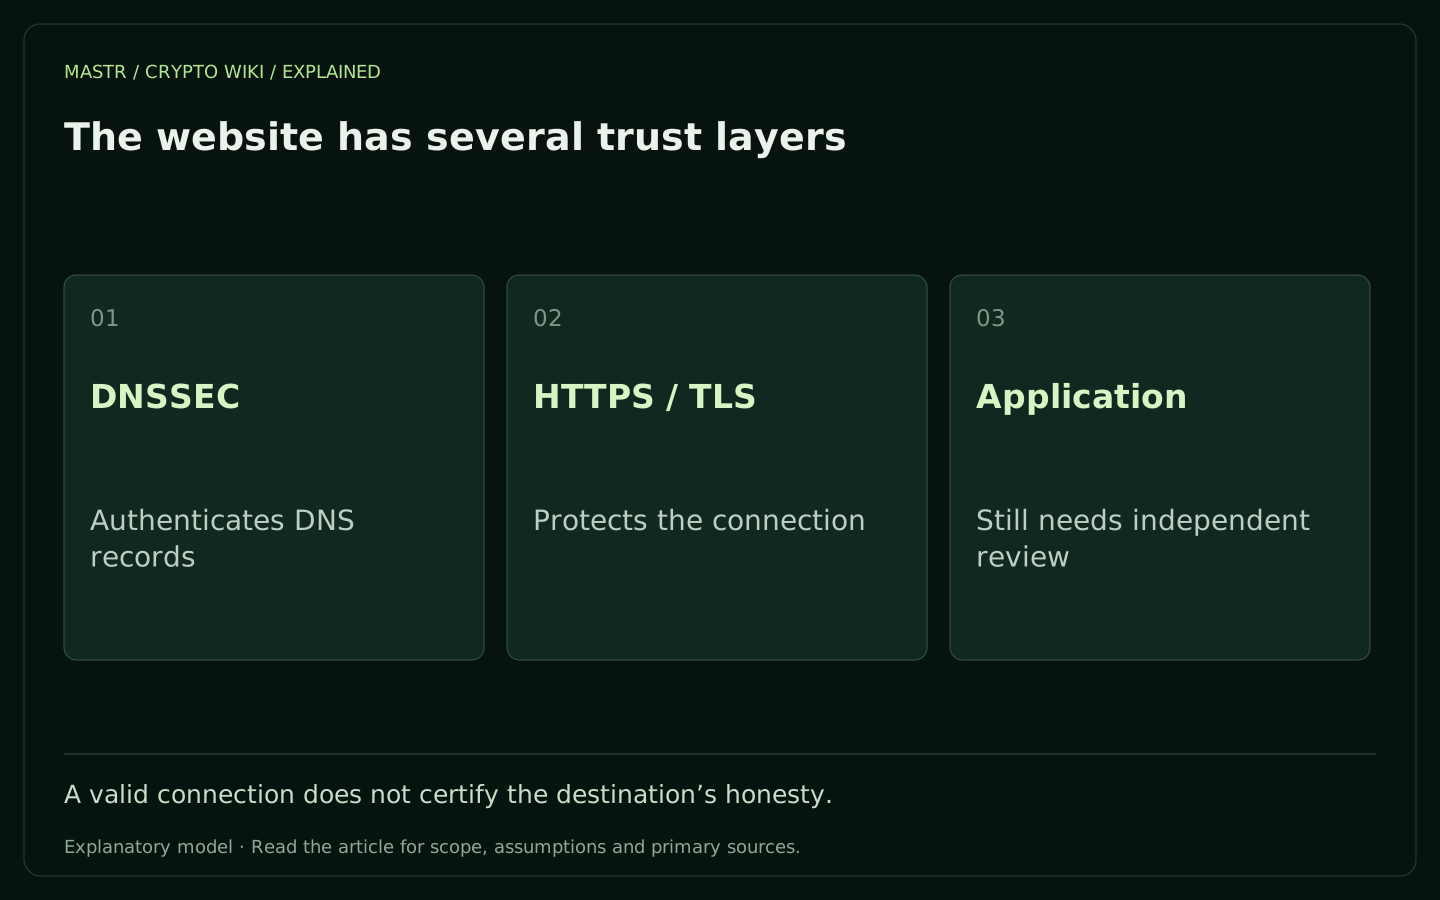
DNS translates a hostname into records used to reach a service. DNSSEC can authenticate signed DNS data through a chain of trust. TLS, used by HTTPS, authenticates the server endpoint under its certificate rules and protects the transport session. These mechanisms address different parts of a connection. A site can use HTTPS without DNSSEC; a signed DNS answer is not encrypted webpage traffic. 1 2
What the padlock cannot tell you
A valid certificate for a lookalike domain does not make it the intended wallet provider. HTTPS can securely deliver a malicious page operated by the holder of that domain. DNSSEC similarly cannot promise that the destination’s application is honest or that its code has not changed. Both protections should be understood as narrow technical assertions, not seals of investment quality.
Where a compromise can still matter
An application has additional dependencies: registrar and DNS administration, hosting, build pipeline, scripts and wallet interaction. Protecting one layer does not remove the others. For readers, carefully verified bookmarks and an independent check of a project’s official domain reduce ambiguity. For operators, documented domain ownership and tested recovery procedures belong alongside server security.
Reporting an incident precisely
Distinguish an incorrect DNS answer, a certificate problem, a compromised web application and a misleading domain registration. They have different evidence and remedies. Record the hostname, time and observed behaviour without converting every suspicious page into a claim that ‘the blockchain was hacked’. A failed certificate check should not be bypassed merely because a social-media post says the website is official.
Exemple concret
A fraudulent site at a different spelling can obtain a valid certificate for its own domain. The browser then encrypts the connection to that fraudulent site correctly. The transport worked; the user’s intended destination was wrong. TLS validation cannot decide that intention.